
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine: Specials Magazine
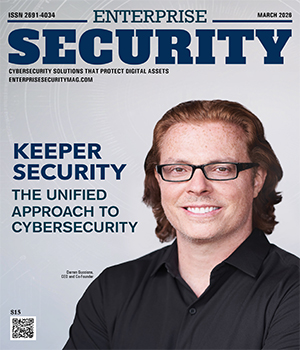
The uncomfortable truth today is that cyber defense has outgrown the product era. What was once a problem of perimeter protection has evolved into a problem of identity, visibility, and control. Attackers no longer batter down the front door; they log in, exploit weak credentials and prey on the blind spots between tools that were never designed to work together. In this environment, layering more products does not reduce risk, but rather, compounds it. This reality is driving a fundamental shift in how security leaders think about privileged access management (PAM). Historically, PAM was built for protecting IT administrators from becoming insider threats. It was siloed, departmental, and reactive. Today, that no longer reflects reality. Privileged access exists far beyond IT, extending into finance, customer support, engineering, contractors, and automated systems. Every user, device and machine identity is a potential entry point for attackers – both internal and external. Keeper Security’s bet is that PAM must evolve from a narrow control into a unified, enterprise-wide platform that governs identity everywhere. Over the past several years, the company quietly rebuilt its architecture around that premise, unifying password management, secrets management, zero trust network access, remote browser isolation and endpoint privilege management into a single system. “The goal was not incremental improvement but structural change: eliminating the seams between tools that attackers routinely exploit. It’s a model designed for how modern environments actually operate, not how security tools have historically been packaged,” says Darren Guccione, CEO and Co-founder of Keeper Security.
Digital Magazine
Web3 Cybersecurity Solution
Quantum computing is significantly transforming the dynamics of IT across industries. However, its potential to break existing cryptographic algorithms necessitates innovations in traditional security systems, which currently safeguard much of the internet. As businesses and governments prepare for a quantum-powered future, the paradigm is evolving toward new opportunities and challenges. Rising to this imperative, Naoris Protocol has pioneered a leap beyond conventional cybersecurity by introducing a decentralized, quantum-resistant security solution. The company integrates blockchain as a core component to protect digital infrastructure across both Web2 & Web3. This approach enables businesses in any sector and vertical to build decentralized networks where data is not stored in a single central location. Naoris Protocol then provides distributed trust, proactive security, and AI-based threat detection. The framework includes post-quantum cryptography integration to ensure protection against quantum computing attacks that could potentially compromise existing cryptographic algorithms and public-key cryptosystems. Naoris Protocol’s resilient Decentralized Physical Infrastructure Network (DePIN) supports next-generation web systems and applications by employing quantum-resistant protocols and a custom-built consensus mechanism called Decentralized Proof of Security (dPoSec). Its decentralized trust mesh architecture transforms devices into trusted validator nodes, eliminating single points of failure and reliance on centralized authority. Together, these systems help companies protect against quantum-based breaches, safeguard IoT ecosystems, and ensure secure communications.
Institutional-Grade Blockchain Solution
Powering the Future of Secure, Scalable Blockchain Solutions Nethermind delivers blockchain infrastructure that enhances security, compliance, and operational resilience for financial institutions and IT teams. As a trusted partner in blockchain adoption, Nethermind delivers institutional-grade security, scalable infrastructure, and compliant financial solutions that connect decentralized technology with enterprisegrade security frameworks. Since 2017, Nethermind has been a driving force in Ethereum’s evolution, working with enterprises, financial institutions, and developers to adopt blockchain technology with confidence, performance, and compliance in mind. From its industry-leading Ethereum Execution Client to institutional staking solutions and real-world asset (RWA) tokenization, Nethermind ensures that enterprises can adopt blockchain securely and at scale. Enterprise-Grade Blockchain Infrastructure As enterprises explore blockchain adoption, stability, security, and compliance are top priorities. Nethermind’s Ethereum Execution Client is trusted by institutions for its reliable, high-performance capabilities. ● Trusted Execution Client: Widely adopted by institutions, optimized for performance, reliability, and secure integration. ● Security & Risk Management: Offering formal verification, cryptographic safeguards, and regulatory compliance features. ● Optimized Blockchain Performance: Supporting enterprises in integrating Layer 2 networks, transaction efficiency, and scalable blockchain infrastructure. Nethermind ensured infrastructure stability during Ethereum’s historic transition to Proof of Stake–one of the most significant upgrades in blockchain history. The company also collaborates with Flashbots, Optimism, Taiko, and Starknet to improve transaction efficiency, security, and blockchain scalability for institutions.
CXO INSIGHTS
Assessment-Backed Cybersecurity for Optimal Use of Resources
Tung Nguyen, Director of Cybersecurity, Denver Water
Turning the Tables on Scammers: Why AI is the Key Ally
Thomas Titus, Director Information Security, Everest
Managing Cost and Data Risk AI and the New Data Privacy Paradime
Richard Mendoza, Senior Director, Data Privacy & Regulatory Compliance, Realogy
The Transition to a Scrum Framework
Lou Windsor, Project Manager, Global Information Technology, Aviagen
Retail under Siege: Evolving Cyber Threats and what we must do next
Mark Alvarado, Executive Director of IT Security & Compliance (CISO), Academy Sports + Outdoors
IN FOCUS
Closing the Gaps in Modern Privileged Access
Modern identity and access management necessitates a shift away from fragmented point solutions that have historically prioritized the technical isolation of IT departments over the broader security needs of the business. Traditional privileged access management (PAM) models often fail because they create visibility gaps where human and machine interactions intersect with legacy infrastructure.
Reducing Security Team Burnout through Intelligent Access Control
Security teams across the region operate under constant pressure. Expanding digital environments, layered regulations, and rising internal complexity have turned access control into a daily source of friction rather than a background safeguard.
EDITORIAL
Governing Access in the Age of Automation
This edition of Enterprise Security Magazine examines a defining shift in cybersecurity: identity has become the new perimeter, and visibility is now the primary control challenge. As environments grow more distributed and threat actors increasingly exploit credential weaknesses rather than infrastructure gaps, organizations must rethink how access, privilege, and enforcement are managed across the enterprise. This shift places governance and identity intelligence ahead of perimeter expansion as the primary determinants of security effectiveness.
Our cover story recognizes Keeper Security, the recipient of the AI-enabled PAM Platform of the Year 2026 award. As detailed in the cover feature, Keeper Security has advanced privileged access management beyond its traditional IT confines into a unified, enterprise-wide identity platform. By integrating password management, secrets management, zero trust network access, remote browser isolation, and endpoint privilege management into a single architecture, the company addresses the fragmentation that attackers routinely exploit. Its zero-knowledge and zero-trust principles eliminate standing privileges and enforce continuous verification, while AI-driven session monitoring enables real-time intervention rather than post-incident analysis. With support for over 80,000 organizations and regulatory authorizations, including FedRAMP High, Keeper demonstrates both scale and operational rigor.
This issue also features critical leadership perspectives on risk alignment and resilience. Tung Nguyen, Director of Cybersecurity at Denver Water, emphasizes the primacy of continuous risk assessment and disciplined prioritization, cautioning against reactive security spending disconnected from business context.
Bringing a financial risk dimension into focus David Finz, Senior Vice President at Alliant Insurance Services, outlines how integrating cyber insurance into incident response planning strengthens organizational recovery and accountability, particularly through predefined vendor coordination and governance clarity.
Together, these perspectives underscore a consistent mandate: cybersecurity leadership today demands unified visibility, disciplined risk management, and integrated response planning. Identity-centric strategy and governance-driven execution now sit at the center of enterprise security, influencing how organizations structure controls, enforce accountability, and adapt to evolving threat conditions.
