THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Ransomware Resilience in Healthcare and Its Impact on Patient Safety
Steve Crocker, Vice President, Chief Information Security Officer at Methodist Le Bonheur Healthcare
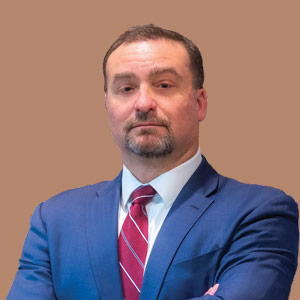 Steve Crocker, Vice President, Chief Information Security Officer at Methodist Le Bonheur Healthcare
Steve Crocker is the Vice President and Chief Information Security Officer at Methodist Le Bonheur Healthcare. With nearly three decades of experience, he oversees a robust cybersecurity program safeguarding patient information. Previously, he transformed the IT infrastructure at Magna Bank. A strategic leader, industry speaker and avid outdoorsman.
Through this article, Steve Crocker emphasizes the critical importance of cyber resilience in healthcare, particularly in the face of ransomware and other cyberattacks. It conveys that cyber incidents can severely disrupt healthcare operations, leading to delays in patient care that could have life-threatening consequences.
Cyber incidents can have a profound impact on any organization. For healthcare providers, the stakes are even higher, as cyberattacks can disrupt operations, incur significant costs, have legal and regulatory implications, and harm an organization's reputation. More critically, they can jeopardize patient safety. Ransomware attacks can have life-or-death implications, making resilience against such threats crucial for healthcare organizations.
When a ransomware incident occurs, systems critical to patient care often become inaccessible. Caregivers may be unable to access vital information such as treatment history, diagnostic images, medication records, and allergy alerts. This can lead to delays or cancellations of medical procedures. In a hospital setting, these delays can be life-threatening. Healthcare providers might be forced to divert incoming emergency patients or transfer existing patients to other hospitals, posing serious risks to patient safety. A notable incident in Germany, where a patient died due to delays caused by a ransomware attack, underscores the potential dangers. Studies have even shown increased mortality rates in hospitals following such attacks. Given these patient safety issues, it's no wonder healthcare cybersecurity is receiving significant governmental attention.
To mitigate these risks, healthcare organizations must implement robust protective measures to reduce the likelihood of cyber incidents. However, it's essential to acknowledge that no defense is foolproof. While cybersecurity teams strive for perfection, attackers only need to succeed once. Therefore, healthcare organizations must enhance their cyber resilience through comprehensive incident response, disaster recovery, and business continuity planning.
“Cyber resilience is an integral component of any information security program, and its significance in healthcare cannot be overstated. The safety of patients depends not only on clinical excellence but also on robust cybersecurity measures.”
Incident Detection and Response
Cyber resilience begins with the ability to detect incidents early in their lifecycle. This requires comprehensive visibility into network traffic and system logs and advanced tools to sift through massive data volumes and correlate events into actionable intelligence. Leveraging third-party partners and AI can significantly enhance this capability.
Organizations must be prepared to act swiftly to contain and eliminate threats. A formal, written incident response plan, supported by detailed playbooks for specific scenarios such as ransomware or DDoS attacks, is essential. Aligning with frameworks like NIST can streamline plan development. While the technical response procedures are crucial, modern security leaders must recognize their role as business leaders and ensure plan development involves collaboration with IT, legal, compliance, communications, clinical areas, cyber insurance, and external counsel. Your response to incidents should include postmortem and lessons-learned meetings. Your plan must also detail communication procedures for your workforce, patients, and external parties such as the media. Predefined communication templates can be helpful. Effective communication during an incident is critical, as organizations are judged on their response rather than the mere occurrence of an incident.
Once the plan is developed, continuous training of key stakeholders is vital. Regular tabletop exercises, both technical and executive, along with real-life simulations, should be conducted as they are essential for the continuous improvement of the plan. It's crucial to have printed copies of the plan and out-of-band communication strategies, as electronic systems may be unavailable during an attack.
Disaster Recovery
Disaster recovery focuses on restoring IT systems to operational status. It begins with a comprehensive Business Impact Analysis (BIA) to assess the criticality of your processes and applications, organizing them into tiers based on importance. Collaborate with business stakeholders to establish recovery time objectives (RTOs) and recovery point objectives (RPOs) that align with executive and board expectations. This prioritization guides IT in determining which systems to restore first. Regular testing of recovery plans is essential to ensure effectiveness, and cloud solutions can offer enhanced recovery capabilities for many organizations.
Business Continuity
Business continuity planning is of paramount importance to board members, as it ensures organizational operations during an incident. In healthcare, this involves maintaining patient care amid disruptions. Clinicians are now heavily reliant on electronic systems, and many have never used manual procedures or haven’t done so in many years. Clinical areas should develop comprehensive downtime procedures. These plans should be kept offline and well-rehearsed. Healthcare electronic systems have become very complex and interconnected, so there is much to consider when planning for downtime events. Periodic system shutdowns to ensure staff can operate without electronic systems like EHRs and email is a good practice for maintaining proficiency in downtime procedures.
Conclusion
Cyber resilience is an integral component of any information security program, and its significance in healthcare cannot be overstated. The safety of patients depends not only on clinical excellence but also on robust cybersecurity measures. Key elements of cyber resilience include executive involvement, cross-team collaboration, leveraging frameworks and third-party partners, maintaining effective communication, and having offline copies and out-of-band communication plans. By prioritizing preparedness and resilience, healthcare organizations can safeguard their systems, and most importantly, protect the lives and well-being of their patients from the growing threat of cyberattacks. In a world where digital threats are ever-evolving, the ability to anticipate, respond and adapt is not just a strategic advantage – it’s a critical responsibility.