
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

Shield Force
Bringing Practical Defensive Cybersecurity Expertise to Latin America
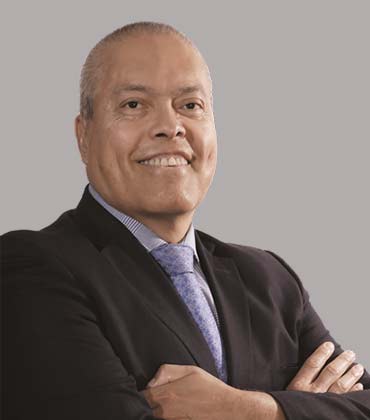 Francisco Javier Villegas Landin, CEO
Shield Force works to close those gaps by providing organizations with defensive cybersecurity capabilities supported by experienced professionals.
The company understands that cybersecurity is not only about deploying technology but also about having the right expertise to identify risks, respond to incidents, and help businesses maintain secure operations.
According to Francisco Javier Villegas Landin, CEO of Shield Force, companies in Mexico continue to face challenges due to lower cybersecurity investment and a shortage of specialized professionals.
The Security Partner For Prevention And Response
Shield Force approaches cybersecurity through three key areas: defensive security, protection and prevention, and managed security services. The company helps organizations prepare for threats through services such as incident response, threat hunting, threat intelligence, malware analysis, digital forensics, data recovery, and endpoint and network detection.
Beyond responding to attacks, Shield Force works with customers to improve their overall security posture. Its preventive services include cloud and AI security assessments, endpoint detection and response, patch management, data loss prevention, encryption, identity protection, vulnerability management, and penetration testing across applications, APIs, and AI environments.
The company also operates cybersecurity monitoring capabilities through its Cyber Security Operations Center, providing continuous visibility and support through device management, event correlation, threat hunting, intelligence, and incident response services.
Security Built Around The Customer Environment
Rather than applying a one-size-fits-all approach, Shield Force begins engagements by understanding each customer’s specific environment. The company assesses existing threats, vulnerabilities, and risks before recommending the controls required to improve protection.
For example, endpoint detection and response, patch management, and data loss prevention solutions are evaluated based on the customer’s exposure and operational requirements. Shield Force also applies technologies such as cloud access security brokers and user behavior analytics to help organizations monitor activity, detect unusual patterns, and prevent unauthorized data access.
This customer-focused process continues throughout implementation. Shield Force defines objectives, develops work plans, establishes service architecture, and works closely with customers to ensure that security improvements align with business needs.
“Cybersecurity is about confidence. Customers need to trust that we will execute correctly, at scale, while prioritizing their operations and honoring our commitments,” says Francisco Villegas.
Execution That Builds Trust
For Shield Force, cybersecurity success depends on reliability. The company believes that customers are not simply looking for tools; they need a partner capable of delivering when security incidents occur and when business operations are at risk.

Cybersecurity is about confidence. Customers need to trust that we will execute correctly, at scale, while prioritizing their operations and honoring our commitments.

“Cybersecurity is about confidence. Customers need to trust that we will execute correctly, at scale, while prioritizing their operations and honoring our commitments,” says Francisco Villegas.
That focus on execution has shaped the company’s customer relationships. Shield Force recently supported a financial organization following a ransomware attack, conducting vulnerability assessments, penetration testing, threat hunting, threat intelligence, forensic analysis, and malware analysis. The engagement helped identify the threat actor, malware, entry point, and patient zero, allowing the customer to address vulnerabilities and improve security controls.
Preparing For The Next Generation Of Cybersecurity
Shield Force continues to invest in emerging cybersecurity capabilities, particularly around artificial intelligence. The company is exploring AIdriven approaches for malware analysis, digital forensics, and threat hunting while preparing services focused on AI security posture assessments and AI-based penetration testing.
Mobile application security has also become an important area of growth for the company. Shield Force provides vulnerability assessments, penetration testing, mobile application protection, mobile device management, and endpoint protection capabilities to help organizations secure increasingly connected environments.
Shield Force has been named as Top Defensive Cybersecurity Services in Latin America 2026, highlighting its continued work in helping organizations strengthen their cybersecurity readiness through practical expertise, responsive services, and customerfocused solutions.
As organizations face a changing threat environment, Shield Force remains committed to helping businesses understand their risks, improve their defenses, and operate with greater confidence.
What to Verify in Latin American Cybersecurity Providers
Cybersecurity buying in Latin America becomes difficult when security coverage expands faster than internal staffing. A provider may offer a broad service catalog yet still leave gaps between detection and remediation. Executives comparing defensive cybersecurity services should look for a model that can connect those stages without creating more handoffs for an already stretched internal team.
Coverage depth matters most when it maps to the attack surface actually in use. Endpoint protection alone does not address cloud applications, mobile access, identity exposure or unmanaged devices. Buyers should examine how a provider assesses the environment before proposing controls, then how it determines where EDR, patch management, DLP, cloud access controls and identity protections belong. The distinction is practical. Buying isolated tools can create duplicate alerts and weak ownership, while a risk-led design makes it easier to assign controls to specific exposure points.
Continuous monitoring also needs scrutiny. A security operations center is useful only when monitoring leads to an action path. Executives should verify whether the provider can correlate events, investigate suspicious behavior, support threat hunting and escalate incidents around the clock. The service model should also make clear who owns containment and what information reaches the customer during an incident. A monitoring contract that stops at alert generation can shift the hardest part of the response back to the buyer. That distinction should be visible in escalation procedures.
Contract scope deserves close reading when multiple security functions sit under one agreement. Response hours, escalation paths, reporting frequency and responsibility for remediation should be explicit before purchase. Otherwise, buyers can discover during an incident that monitoring coverage is broader than the provider’s authority to contain or correct the underlying problem.
Implementation discipline can be as important as the technology itself. Defensive programs often touch workstations, servers, cloud platforms and user activity, which means weak scoping can disrupt business systems or leave controls partially deployed. Buyers should expect an initial assessment, defined objectives, implementation requirements and a work plan that can be refined before execution. Deliverables should also show what changed in the environment rather than simply confirm that a tool was installed. Clear ownership during rollout also reduces delays when technical dependencies or access requirements surface.
Specialized areas can narrow the field further. Mobile application security, forensic analysis, continuous exposure management and AI-related security testing require different skills from routine device monitoring. Buyers with these requirements should determine whether expertise is available within the provider or depends on outside escalation. The same applies to incident response. A provider that can move from detection into investigation and remediation support can reduce the number of parties involved when an attack is already underway.
Shield Force begins engagements by assessing the customer environment and defining the controls required before implementation. Its defensive services include EDR, DLP, patch management, cloud access security controls and identity-related protections, supported by 24/7 monitoring through its cybersecurity operations center. It also provides threat hunting, threat intelligence, forensic analysis and incident response support, while extending coverage to mobile application security and continuous exposure management. This breadth is most relevant for buyers that need one provider to handle prevention and monitoring through investigation and response without handing each stage to a separate specialist. For organizations in Latin America with limited internal security staffing, Shield Force warrants evaluation where execution depth matters as much as tool coverage.
...Read more
Company
Shield Force
Management
Francisco Javier Villegas Landin, CEO
Description
Shield Force helps organizations across Latin America address evolving cyber threats through defensive cybersecurity services, including threat hunting, incident response, security assessments, managed security operations, and AI-driven solutions designed to improve resilience, protection, and operational confidence.
