
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

PAGO Networks
Combining AI and Human Expertise for the MDR Landscape
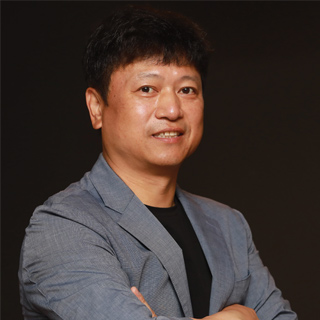 Paul Kwon, CEO
While most endpoint detection and response (EDR) solutions rely heavily on AI, PAGO’s focus on human intelligence ensures precise identification of malicious activity and accurate validation of cybersecurity implementations. Its distinct combination of powerful AI intelligence solution including & not limited to Cylance for OT Environment, SentinelOne & Stellar Cyber XDR with human expertise transforms enterprise-managed detection and response MDR. For Cylance, one of the first AI-powered antivirus solutions, PAGO developed a threat validation process that automated the scaling process, which involved automatically detecting and capturing suspicious activity, then employing a seasoned professional to confirm malware.
On the backend, its indicator of compromise extraction goes beyond traditional detection to actively address malware infiltration. Building on this approach is DeepACT, a managed threat detection and response service platform that engages in threat hunting indicators of attack (IOA) arising from seemingly normal login activities.
In addition to preventing malicious activities through timely IOA detection, DeepACT simulates attacks to identify vulnerabilities and understand how malware could penetrate an infrastructure. This proactive approach disrupts an attacker’s foothold before a successful payload execution. A strong focus on these early stages ensures that even sophisticated threats are intercepted before they cause significant harm.
Taking it further, the company shares the IOAs with its customer community to inform all members about the potential threats. Meanwhile, DeepACT performs continuous monitoring and response, attack surface management, as well as breach and attack simulation.
“DeepACT provides actionable insight into the root cause and penetration methods, which can safeguard your cloud environment with strong risk mitigation,” says Paul Kwon (YoungMok Kwon), CEO of PAGO Networks.
Equipped with these capabilities, DeepACT provides comprehensive visibility and active response to secure the operational technology (OT) environments across semiconductor, chemical and energy manufacturers. Its impact is incredibly profound within air-gapped infrastructures exposed to external networks. The platform caters to the lateral movements of ongoing network traffic in on-prem data centers, cloud servers or Kubernetes to block internal and external botnet attacks on end users.
A notable case was one from 2020 when a major car parts manufacturer faced a critical machine ransomware attack on 5,000 workstations and over 200 servers. Since their existing security partners could not mitigate this issue in the optimum time, PAGO stepped up, prioritizing the importance of how a solution is used rather than just the type of cybersecurity implemented.
Equally impressive is PAGO’s on-site threat cleaning services, which uncover numerous malware instances that have evaded detection. Since legacy OT and IT systems have a fixated nature and limited scope for integrating cybersecurity frameworks, PAGO deploys suitable AI-based endpoint protection to fit various infrastructure security requirements. By providing this service without any purchase conditions, PAGO builds trust among clients and enables them to confidently adopt its full-service.
A boutique firm based in South Korea, PAGO has expanded to eight Asian countries, including Singapore, Indonesia, the Philippines, Thailand, Malaysia and Vietnam. In these geographies, it directly assists customers suffering from cybersecurity incidents with ‘freemium’ threat detection and cleaning services. The company’s reliability and accountability have helped maintain a 99 percent retention rate across more than 400 customers.

DeepACT provides actionable insight into the root cause and penetration methods, which can safeguard your cloud environment with strong risk mitigation

A notable case was one from 2020 when a major car parts manufacturer faced a critical machine ransomware attack on 5,000 workstations and over 200 servers. Since their existing security partners could not mitigate this issue in the optimum time, PAGO stepped up, prioritizing the importance of how a solution is used rather than just the type of cybersecurity implemented.
It provided comprehensive MDR tools for their OT and IT environments and deployed on-site analysts and support from a remote facility. The team resolved numerous issues, including existing malware, unknown virus scanning tools, external breaches into the server, and SMTP-based brute force attacks. One of its recommendations included changing account passwords and turning off file-sharing applications or portals that exposed assets to the internet. Within one month of continuous monitoring and attack response, PAGO eradicated the ransomware and ensured their environment remained attack-free. Following this successful incident response, the client implemented PAGO’s MDR capabilities across their entire network without the need for separate testing.
Building on a wealth of successes like this, PAGO is set to continue blending advanced AI with human expertise to help security personnel cut through the noise and effectively counter real threats.

Company
PAGO Networks
Management
Paul Kwon, CEO
Description
In a landscape with endless security alerts, PAGO Networks’ distinct combination of powerful AI intelligence and human expertise transforms enterprise-managed detection and response (MDR). While most endpoint detection and response (EDR) solutions rely heavily on AI, its focus on human intelligence ensures precise identification of malicious activity and accurate validation of cybersecurity implementations.

