
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

P0 Security, Inc.
Leading the Charge in the Evolution of Privileged Access Management
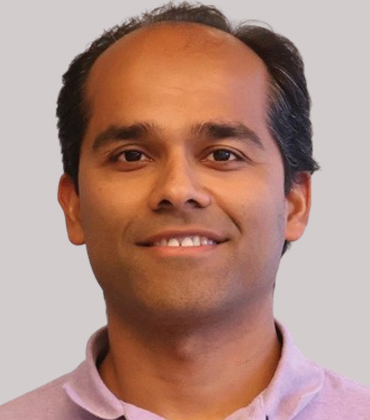 Shashwat Sehgal, CEO and co-founder
Securing privileged access in enterprise environments has long been compared to defending a medieval castle. In that analogy, the moat represents network perimeter controls, such as VPNs, designed to keep attackers out. Vaults safeguard the keys, storing credentials that grant entry once the perimeter is crossed.
This model worked well for static, on-prem environments, where controlling access at the edge and protecting credentials addressed most risks. In today’s digital castle, the moat is not enough on its own. Traditional network controls and authentication are necessary, but they don’t solve authorization and least privilege in cloud environments.
Vault-first can still make sense for static on-prem or air-gapped environments and for systems that don’t support modern authorization controls. The gap is cloud and dynamic infrastructure, where access needs to be time-bound, just enough and provably governed.
P0 Security helps control and audit access inside the castle, deciding who can enter which room, for how long, and under what conditions, after the moat has already been crossed.
Co-founded by Shashwat Sehgal, P0 Security is identity-native and cloud-native, designed to secure permissions across AWS, GCP and Azure. The company focuses on modern authorization-based controls, shifting attention from network and authentication layers to the lifecycle of access itself.
Sehgal’s journey into privileged access management began with a simple realization: the systems many organizations relied on were built for a different era. “We are a company that helps organizations control the access of any identity, whether it’s a user, workload, or agentic identity, to sensitive infrastructure or assets,” he says.
Offering Lifecycle Governance
How does lifecycle-based authorization improve control over access in complex enterprise systems?
As enterprises adopt cloud-native technologies and face the explosion of agentic identities, such as AI-driven agents and workloads, securing access through older approaches becomes increasingly difficult. Traditional network controls and authentication are necessary, but they don’t solve authorization and least privilege in cloud environments.
P0 Security focuses on the authorization lifecycle: approve, grant short-lived access, then revoke it automatically. That approach reduces the attack surface by reducing or eliminating standing privileges where possible.
For organizations trying to bring order to complex environments, the starting point is visibility. Many teams still lack a clear picture of who has access to what, across identities, resources and entitlements. As Sehgal puts it, “If you ask an arbitrary enterprise customer, they’ll probably say that we have no idea whether our access is under control or not.”

We are a company that helps organizations control the access of any identity, whether it’s a user, workload, or agentic identity, to sensitive infrastructure or assets.

For organizations trying to bring order to complex environments, the starting point is visibility. Many teams still lack a clear picture of who has access to what, across identities, resources and entitlements. As Sehgal puts it, “If you ask an arbitrary enterprise customer, they’ll probably say that we have no idea whether our access is under control or not.”
The first step is understanding access permissions across identity providers such as Active Directory, Okta and Azure, along with cloud platforms such as AWS and GCP. From there, P0 helps organizations rationalize access and apply policy so permissions are temporary, tightly scoped and aligned with least privilege. The result is more control and audit-ready access records.
A critical part of P0 Security’s approach is identity provider-native authorization. While legacy approaches often rely on shared secrets or static credentials, which create security and operational risk, P0 emphasizes identity-native methods for provisioning access. As Sehgal notes, “Shared secrets and static credentials are probably the single biggest threat vector,” and they also create credential rotation fatigue for security teams.
Helping Clients Look Beyond the Traditional Feature Checklist
What challenges exist in standardizing authorization across diverse cloud and identity systems?
P0 Security also addresses the architectural challenges involved in building an effective authorization control plane. In cloud environments, every system can define and enforce access differently, which makes policy difficult to standardize. P0 has focused on building a model of entitlement management that can bring those patterns into a consistent framework.
“Our corporate customers can easily use them in their environments,” says Sehgal, underscoring the practical goal behind the product design.
As businesses evaluate modern privileged access management tools, Sehgal encourages them to move beyond feature checklists and ask how access is actually governed. One of the first questions, he says, is simple: “What is your model of governing access? Are you vault-based, or do you generate just-in-time and just-enough privileges for every identity?”
P0 Security differentiates itself by offering an agentless solution that can be deployed in minutes rather than months and integrated across a wide range of cloud services and identity systems.
Preparing for the Next Wave of Growth
Why will non-human identities drive future challenges in privileged access management systems?
One of the common problems with legacy PAM systems, Sehgal says, is poor user experience, which can limit adoption among development and IT teams. P0 Security has worked to make its platform unobtrusive and simple to use so developers can gain access quickly without slowing their workflow or compromising security.
In practice, that means access that is short-lived, tightly governed and tied back to identity-provider-native records rather than standing permissions that linger indefinitely.
One of P0’s larger clients, a B2B SaaS technology company, replaced a legacy PAM solution with P0’s agentless platform after recognizing the need for authorization-based access. Developers were able to gain just-in-time, short-lived access to production systems across multiple cloud providers while sensitive access remained governed and auditable.
In the near future, Sehgal expects the next wave of privileged access challenges to come from non-human identities. “The next wave of growth is going to come from not just users, but increasingly workload identities and then agentic identities,” he says.
As those identities proliferate, organizations will need the same discipline they apply to human access: understand what access exists, right-size it and enforce time-bound authorization by default. In that model, the focus is less on selling a promise and more on maintaining a clear, defensible record of who can do what, when and why.
Rethinking Privileged Access in the Cloud Era
Privileged access management has existed for decades, yet its original assumptions no longer hold. Early enterprise environments were centralized, static and perimeter-based. Access control revolved around VPN gateways and password vaults, mirroring a castle-andmoat model in which entry to the network and possession of credentials signaled trust. That approach made sense when infrastructure lived in a single data center and privileged accounts were few.
Cloud adoption, elastic workloads and the rise of machine identities have disrupted that model. Modern environments span multiple cloud providers, identity systems and dynamic services. Human users, service accounts and software agents interact with sensitive systems at scale. In this context, network controls and stored credentials offer a false sense of control. Once inside the perimeter, excessive or standing privileges often persist, invisible to security teams and difficult to rationalize.
Executives evaluating privileged access platforms should therefore look beyond vault features and session brokering. The core question is whether a solution governs authorization itself. It is no longer sufficient to manage passwords or mediate connections. Enterprises need a clear, consolidated view of who or what has access across identity providers and cloud services, followed by the ability to rationalize that access into short-lived, least-privilege entitlements. Persistent administrative rights, even if well monitored, represent latent risk.
Architectural design also deserves scrutiny. Many legacy tools require dedicated infrastructure, bastion hosts or complex agents that take months to deploy and tune. Such implementations can delay value realization and create friction between security purchasers and engineering users. A modern approach should integrate directly with cloud control planes and identity providers, minimizing operational overhead while preserving native identity context. When access is tied back to the enterprise identity system rather than shared accounts or static credentials, auditability improves and governance teams can attribute actions to specific users or workloads without reconstruction exercises.
Breadth and consistency of coverage matter as well. Enterprises rarely operate a single cloud or a single access path. Developers may need shell access to virtual machines, temporary elevation within Kubernetes clusters or limited entitlements to managed services. Workloads may request permissions programmatically, and AI-driven agents are beginning to consume data autonomously. A viable platform must abstract these diverse authorization models into a consistent control layer without forcing teams to sacrifice native capabilities. Depth of integration across cloud providers and services is essential to prevent fragmented governance.
P0 Security positions itself squarely in this authorizationfirst model. Rather than centering on vaults or network gateways, it focuses on governing privileged access at the entitlement layer. It connects directly to cloud environments and identity providers, building a consolidated view of access across systems. From there, it enables short-lived, just-in-time privileges for users, workloads and emerging agent identities, eliminating standing access where feasible. Its agentless deployment model reduces infrastructure burden and accelerates rollout, while preserving native identity attribution for audit and compliance purposes.
For enterprises operating dynamic, multi-cloud environments, an authorization-centric platform aligns more closely with current risk patterns than legacy vaultbased tools. P0 Security stands out for its focus on leastprivilege access, rapid deployment and comprehensive coverage across human and non-human identities. Organizations modernizing privileged access controls should place it at the top of their shortlist when replacing perimeter-era approaches with cloud-native governance.
...Read more
Company
P0 Security, Inc.
Management
Shashwat Sehgal, CEO and co-founder
Description
P0 Security, led by CEO Shashwat Sehgal, is transforming privileged access management with an authorization-focused approach, moving beyond traditional network and authentication controls. Their platform helps enterprises manage sensitive access securely, efficiently and consistently across complex cloud environments.

