
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
A featured contribution from Leadership Perspectives, a curated forum for enterprise security leaders, nominated by our subscribers and vetted by the Enterprise Security Magazine Editorial Board.

Head Of Information Security at the International Development Bank
Cyber Security in the Finacial Sector
Introduction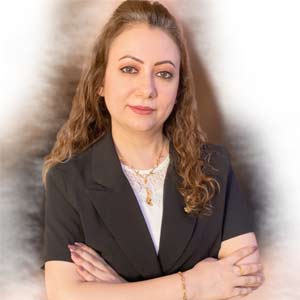 Amani Alhasoon, Head Of Information Security at the International Development Bank
In today's digital age, banks and other financial institutions have become majorly dependent on technology to ensure the delivery of featured services to their customers. However, this dependence also exposes the financial sector to many cyber threats and vulnerabilities. Ensuring cybersecurity measures has become a priority for financial institutions as they are attractive targets for cybercriminals aiming to steal sensitive information, disrupt services or exploit vulnerabilities for monetary gain. This article sheds light on essential strategies to boost security measures.
Understanding the Cyber Threat Landscape
Cyber threats targeting the financial sector are becoming increasingly sophisticated and persistent. From ransomware attacks to social engineering and phishing scams, data breaches, identity theft, and financial fraud, cybercriminals are evolving new technic every day, new ways to exploit vulnerabilities. As a chief information security officer, staying ahead of these threats and implementing proactive defense strategies is an everyday challenge.
“Constant Technological Advancements Provide Both Opportunities And Challenges In The Financial Sector”
Developing a Comprehensive Cybersecurity Strategy
To effectively defend against cyber threats, a thorough cybersecurity strategy must be implemented, and here are the key areas to concentrate on:
● Establishing a Culture of Cyber Awareness: Education and awareness play a role in mitigating cyber incidents. As the chief cybersecurity officer, I prioritize the significance of providing cybersecurity training to every employee. It is essential to foster a culture of vigilance, urging them to report any security breaches.
● Implement robust Access control: Effective access controls are mandatory to prevent unauthorized access to sensitive information. As a chief information security officer, I highly recommend using multi-factor authentication, enforcing a strong password policy, and implementing role-based access control with the least privilege principle to ensure that only authorized individuals can access the required system.
● Network Monitoring and Threat Detection: Advanced threat detection systems, log collection and correlation, and network monitoring tools are playing a great role in identifying unusual behavior or anomalous activities that may lead to potential security breaches. By continuously monitoring the network, we can respond promptly to cyber incidents and effectively contain them.
● Establish a comprehensive Incident Response Plan: It is important to have a proper incident response plan in place to minimize the consequences of a cyber incident. The incident response plan should be implemented and at least includes the following:
● Defined clear roles and responsibilities
● communication channels to ensure effective coordination
● Specific incident response procedures
● Business recovery and continuity procedures
● Reliable data backup processes
The lessons learned from past incidents should be considered to ensure the effectiveness of the incident response plan.
Compliance and Regulatory Measures in the financial sector
Compliance is directly tied to cybersecurity. While understanding and implementing multiple cybersecurity practices can be complex, compliance requirements offer a built-in cybersecurity framework. However, It is important for us to recognize the significance of adhering to these regulations By following them, such as the Payment Card Industry Data Security Standard (PCI DSS), ISO/IEC 27001, and the National Institute of Standards and Technology (NIST), so If the organization is compliant we ensure that it fulfills its commitments and engenders trust among stakeholders.
Conclusion
Constant technological advancements provide both opportunities and challenges in the financial sector. As chief information security officers, our role is to lead our organizations to safe ground and get top management support by following the previously mentioned steps besides investing in cutting-edge technologies to enhance our threat detection capabilities and protect sensitive financial data and maintain the stability and integrity of the financial sector.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
