
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
A featured contribution from Leadership Perspectives, a curated forum for enterprise security leaders, nominated by our subscribers and vetted by the Enterprise Security Magazine Editorial Board.

Natera
Building Lean Security Program to Accelerate Business Growth
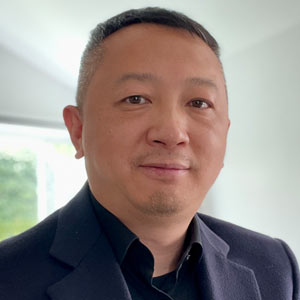 Bill Yue Chen, Chief Information Security Officer, Natera
As the Chief Information Security Officer (CISO) at Natera, Dr. Bill Chen is responsible for managing an enterprise-wide cybersecurity program that encompasses strategic, governance, risk and compliance (GRC), data protection, and product security. Prior to joining Natera, he held different executive and technical positions at VISA, Palo Alto Networks, Cisco, Microsoft, and Coupang. With over two decades of experience in cybersecurity, he is also a successful start-ups advisor, a public speaker, and an author of multiple publications and patents. In his spare time, he plays guitar and enjoys the outdoors.
What are some of the challenges impacting the security space?
In today's rapidly evolving world, significant transformations have continuously reshaped the security industry. These changes include the rapid increase in remote work, the impact of geo-political tensions and warfare, the constant evolution of AI technologies, the changes in laws and regulations, and the expanding attach surfaces due to cloud and IoT applications usage. For security leaders, the ability to prioritize effectively in this dynamic landscape with considerations to the business context has become mission critical.
What are some of the latest trends in the security space today?
The following list is not intended to be exhaustive, but some of the key observations. (1) the shifting geopolitical landscape has changed the priority for many organizations to implement compliance, data protection, supply chains, and other security controls; (2) The evolving AI and ChatGPT technology has opened new possibilities for cyber-attacks. For example, the threats posed by misinformation, AI-powered phishing, and next generation BOTS are rapidly growing; (3) The surge in Cybercrime-as-a-Service (CaaS) has become more and more mature and easily accessible to many hackers; (4) On the other hand, the security talent shortage will persist due to the accelerated wave of digital transformation and expanding threat landscape. It will continue to be a tight race between attackers and defenders.
"Security is an art of prioritization and decision-making"
What are some of your recent project initiatives?
Doing more with less is paramount in today's economic climate. Our recent initiatives have centered around a few critical pillars: (1) Enhancing visibility across data, assets, users, and third-party dependencies to proactively identify and prioritize security vulnerabilities; (2) Implementing robust security measures and governance frameworks to fortify our defense through a layered defense-in-depth approach; (3) Sustaining continuous monitoring, rigorous testing, and adaptive hardening techniquest; (4) Enhancing awareness training based on threat landscape observations. These initiatives are seamlessly integrated within our zero-trust strategy, empowering us to establish a lean security program while optimizing our cyber defense capabilities.
How do you envision the future of the space?
The cybersecurity space will continue to be dynamic and transformative. Compared to the past decades, the geopolitical factors are shifting business priorities, regulations, and threat landscape. The cyber threats have poised to be much more sophisticated than ever before due to technology advances in AI. The shortage of skilled cybersecurity professionals will persist. There will be no one-size-fits-all solution or perfect security. Instead, it is very important for security leaders to deeply understand the economics of cybersecurity within the unique business context, so that they can optimize strategy, decision-making, and operations by effectively navigating the interplay of technology, people, and process.
What would be your piece of advice for budding professionals in the field?
“Prioritization, prioritization, prioritization.” Security is an art of prioritization and decision making. To a certain extent, many incidents could have been prevented had the issue been prioritized even a single day before the breach occurred.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
