
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
A featured contribution from Leadership Perspectives, a curated forum for enterprise security leaders, nominated by our subscribers and vetted by the Enterprise Security Magazine Editorial Board.

CEO of Strategic Cyber Ventures
Breaches, Bailey, And The Board Member: A New Way To Ally Your Board Of Directors And Employees With Your Security Team Wc: 1011
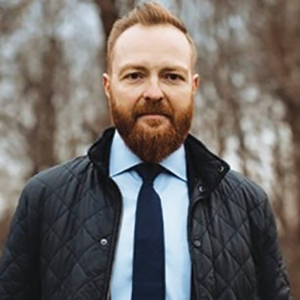
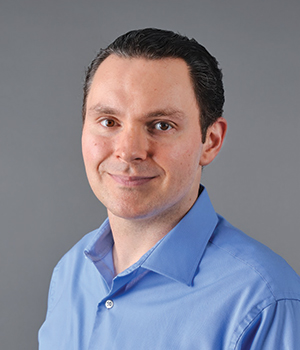 Steve Thomas, Co-Founder and CEO of HackNotice and Hank Thomas, CEO of Strategic Cyber Ventures
It’s hard enough getting 9-5 employee, Bailey Smith, to comply with security policies and practice good cyber hygiene, but what can be even tougher is pushing corporate Board members to meaningfully understand and engage with an organization’s security operations. Often, when breaches occur, Board members are, for various reasons, reluctant to participate in material communication with their company’s security specialists to better understand the situation and help quickly resolve the problem. Like employees, Board members defer complex and cumbersome security issues to the security team, too often. This problem is compounded when the security team does not have senior representation on the Board. This is akin to police trying to solve a rash of burglaries without the participation of the homeowners, landlords, tenants, or neighbors affected.
Board members’ reluctance to get meaningfully involved with security issues impacts the ability of their companies to solve smoldering and immediate security problems, improve their security posture, and prevent future breaches. Lack of involvement creates a constantly growing knowledge gap that leads to communication breakdowns, lack of trust, misaligned resources, and an inability on the part of the security team to confidently respond to ongoing and future breaches. Additionally, breach-related boardroom passivity can reduce the effectiveness of security-related external communications to shareholders and customers, damaging trust and potentially tarnishing a brand. To implement the most rapid and effective response possible, Board members need to be materially involved with their security team and company leadership during the critical period after a breach. When a cyber-attack occurs, the Board members are the last people you want left in the dark about the impact of the event and the details of their security team’s response.
The 2017 Equifax breach, which resulted in the personal information of almost 150 million Americans being leaked, is now widely understood to be one of the first extensively publicized examples of the consequences of cybersecurity non-involvement by a major Board of Directors. As The Harvard Law School Forum on Corporate Governance says notes:
“Boards must set more granular expectations for CEOs and senior leadership teams, whether or not the law requires it to do so. Advances in technology which not only increase the risks of cyber security issues, but also contribute to the rapidity with which information is disseminated, and the acceleration of business operating cycles means that Boards must be much more engaged with their senior teams if they are to avoid, at a minimum, reputational damage from failure to engage, much less the potential for adverse legal consequences. Equifax is not an isolated example of potential lack of Board engagement.”
 Solutions
So much has improved since the 2017 Equifax breach, but much more needs to be done. There are now rapidlyemerging innovative approaches that can automate the push toward highly relevant cybersecurity threat awareness data, and immediate, easyto-perform remediation actions from the Board to Bailey’s cubicle. These approaches create a straightforward and personal cyber threat operating picture for members of a company outside of the security team. Board members should have a way to engage with the security team—and company security culture in general—on a regular basis, so that they stay up-todate on security events, and also hone their own knowledge of security work. Security should be taken as seriously as any other issue the Board deals with, if not more seriously.
"Board Members Should Have A Way To Engage With The Security Team—And Company Security Culture In General—On A Regular Basis, So That They Stay Upto-Date On Security Events, And Also Hone Their Own Knowledge Of Security Work"
Boards should obviously understand the major implications, both financial and reputation-related, of a breach. Security teams can help, by being good translators of technical cyber events and the current security environment. But it’s even better if Board members continuously educate themselves about the current state of the security industry and important recent cyber events (both inside and outside of the organization).
Reputation Damage
Like thousands reading this piece, the authors have been victims of high-profile breaches that initially went unreported. Hank Thomas, already a victim of the 2014 U.S. government's Office of Personnel Management (OPM) breach, and Steve Thomas were both victims of the 2017 Equifax breach. The experience was a particularly raw one for Steve, as he bore witness to how little control people have when it comes to relying on corporations to inform them of breaches. Steve recounts how Equifax explicitly told him that his data was safe after the breach but, then, came back months later and informed him that he was indeed actually compromised. It was, for Steve, the breaking point. Already in the security industry, Steve and Hank both subsequently founded companies focused on better defending and automating the cybersecurity world. Steve set out to build a threat awareness platform that offered personalized, real-time, actionable updates about breached data to everyone, from individual everyday users all the way up to chairmen of boards and beyond—so they no longer have to rely on corporate press releases, lawyers, or news articles to find out about breaches.
Conclusion
Corporate Board members can no longer afford to absolve themselves of responsibility for their organization’s cybersecurity. Hiding behind lawyers who shield them from the truth about a damaging breach is no longer a viable course of action. Board members have to be the most informed they can be in order to fulfill their fiduciary duty. Regulators, customers, shareholders, and security teams and employees expect that leaders at the top will have a firm grasp on all company operations. Increasingly, cybersecurity is becoming a competitive differentiator for companies, and recovering from reputation-damaging cyber events is expensive, time-consuming, and possibly fatal to the firm. Board members need to take proactive steps to continuously stay threat-aware and up-to-date on modern cybersecurity best practices. They also have the duty to provide their employees on the front lines of enterprise security risk management with the tools and training to keep them threat-aware, practicing good cyber hygiene, and in-sync with others in the firm via a common threat awareness platform. Through this, Board members can involve themselves fully with security and IT teams in the event of a cybersecurity threat.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
