
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
A featured contribution from Leadership Perspectives, a curated forum for enterprise security leaders, nominated by our subscribers and vetted by the Enterprise Security Magazine Editorial Board.

The Estée Lauder Companies
A Look at Cyber Security and Machine Learning.
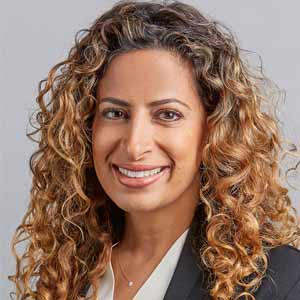 Nada Noaman, Chief Information Security Officer and SVP, The Estée Lauder Companies
Nada Noaman, one of the eminent personalities in the cybersecurity space is currently excelling as a Chief Information Security Officer and SVP at The Estée Lauder Companies. She brings over her twenty-three years of experience in cybersecurity space to lead cyber and risk initiatives across ELC’s global brand. Throughout her career journey, she served as Cybersecurity VP at AT&T/Warner Media, Deputy CISO at Warner Bros, and Director Cybersecurity and Risk at PwC.
Please share with our readers your current roles and responsibilities in the organization.
As a Chief Information Security Officer at Estee Lauder Companies, I have a broad range of responsibilities for cyber and information security as well as governance, risk, and compliance. This includes overseeing cybersecurity operations and response, engineering and architecture, governance, risk & compliance, data security and protection, and a few other budding programs that are currently in development. My responsibilities do not just end there. One of my primary objectives is to lead and secure Estee Lauder Companies and all of our brands holistically, which involves prioritizing by risk, compliance and meeting regulatory requirements, and creating a long-term vision of how we secure the company. Whether it's e-commerce, manufacturing, or retail we are committed to securing every aspect of the business.
What are some of the metrics used to measure the effectiveness of the cybersecurity programs implemented in your organization?
When it comes to measuring the effectiveness of a cybersecurity program - the foremost metric anyone should consider are operational: any and all incidents and events, and the impact it can cause. This also includes how prepared your cybersecurity team is for any attack, how quick the response is, and how fast the threat was neutralized. The second is stakeholder feedback – are you truly serving the business and its mission, and the last is employee engagement and attrition- where in today’s market, it is crucial to create a culture and environment that is collaborative, growth-oriented, and filled with opportunity for growth and knowledge-sharing in order to attract, grow, and retain the best talent. To me, these are the biggest signs of a successful program- the rest of your KRIs and KPIs are complementary.
How do you ensure the organization complies with rules and regulations such as GDPR, HIPAA, and PCI DSS?
In order to ensure that we comply with the rules and regulations, it's crucial that we partner with our colleagues in privacy, legal, compliance, and internal audit. We have a dedicated compliance program that's made up of different SMEs in each framework. So whether it's PCI DSS or international security regulations there are a bunch of different laws that we need to keep up with. Therefore, it is our mission as compliance professionals to summarize each requirement and holistically develop a program that not only complies with them but actually embeds those requirements into our own requirements as well.
“With AI capabilities being improved drastically, humans will experiment with and ultimately rely on AI in a new way. However, with automation on the rise, we need to keep up, which forces us to think more creatively and strategically about what sources of AI we rely on, what we feed it, and how we leverage it securely.”
Can you please share some of the misconceptions seen in the cybersecurity industry and they are addressed?
The most common misconception we hear is that security teams are trying to slow things down. We are here to help enable the business, without them, we’re securing for security’s sake. Without us, well, we won’t go there. It is critical that we adapt to new strategies and deploy various controls and tools over time. Technology is everchanging and ever advancing. We have to remember that failing to be agile and responsive may result in building security measures too slowly for rapidly evolving threats. Many also believe that it is the sole duty of the cybersecurity team to keep the entire workforce secure. Even though it is true to an extent, without the help of each and every employee that has access to the network, maintaining a strong cybersecurity network is impossible.
How do you envision the future of cybersecurity space in the following years?
With AI capabilities being improved drastically, humans will experiment with and ultimately rely on AI in a new way. However, with automation on the rise, we need to keep up as fast as possible, which forces us to think more creatively and strategically about what sources of AI we rely on, what we feed it, and how we leverage it securely. The new trend in cybersecurity is the increased use of AI and machine learning by both companies and adversaries. With more publicly available information, more AI can ingest all sorts of available data leading to a higher risk of being exposed to and targeted by threat actors. There is an ever-growing need for companies to be prepared and proactive in their cybersecurity efforts instead of ignoring or denying the potential risks.
What is your piece of advice to budding professionals in the cybersecurity space?
It is important not to give up. There are plenty of opportunities in the cybersecurity space and there are a whole lot of opportunities to learn too. Always be prepared to do the work, and always remember the experience we acquire from any role aggregates into qualifications and diversity of thought. There is no one path to growth. Remember that cross-training and gaining experience in all aspects of cybersecurity, compliance, and risk is crucial for becoming a qualified and effective leader. As a leader, I feel it's important to create a culture that fosters innovation and diverse perspectives, allowing every member of the organization to have opportunities to grow.
The articles from these contributors are based on their personal expertise and viewpoints, and do not necessarily reflect the opinions of their employers or affiliated organizations.
