THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

Fireeye
Delivering Advanced Detection And Prevention Capabilities
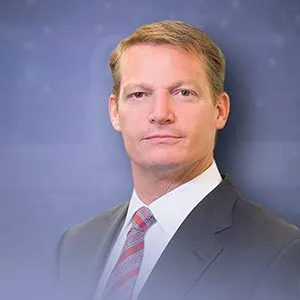 Kevin Mandia, CEO
Enter FireEye.
FireEye Endpoint Security delivers advanced detection and prevention capabilities to help respond to threats that can bypass traditional endpoint defenses. With the addition ofantivirus (AV) and malware detection capabilities for known threats, machine learning
and behavioral analysis for unknown threats along with endpoint detection and response (EDR) capabilities, analysts can now rely on a single endpoint agent for expanded visibility to quickly determine the exact scope and level of attack activities related to both known and unknown threats. With detailed context on blocked and unknown threats, analysts can adapt defenses to all cyber attacks. FireEye Endpoint Security defends against today’s cyber-attacks by enhancing the best parts of legacy security products with FireEye technology, expertise and intelligence. Using a defense-in-depth model, the modular architecture of Endpoint Security unites default engines and downloadable modules to protect, detect and respond, and manage endpoint security.
To prevent common malware, Endpoint Security uses a signature-based endpoint protection platform (EPP) engine. To find threats for which a signature does not yet exist, MalwareGuard uses machine learning seeded with knowledge from the frontlines of cyber-attacks. For attacks on exploits in common software and browsers, ExploitGuard uses a behavioral analysis engine that determines if an exploit is being used and stops it from executing. In addition, FireEye continuously creates modules to detect against attack techniques and accelerate responses to emerging threats. For example, ProcessGuard was developed to stop credential exfiltration.
Making IT assets Available, Highly Functioning, and Secure
FireEye Endpoint Security uses multiple protection engines and customer deployable modules built from the experience of front-line responders to defend against these types of attacks. The combination of signature-based, machine-learning based, and behavioral-based protection capabilities, the UAC Protect module, and the Process Guard module for FireEye Endpoint Security provide maximum protection for customers.
The Process Guard module for FireEye Endpoint Security can protect against common credential dumping attacks so it’s important to download, install, and enable the Process Guard module for FireEye Endpoint Security. FireEye Endpoint Security can also be configured to alert based on IOC detections related to DARKSIDE and other similar threats. In order to enable that functionality, follow the steps below to ensure that Real-Time Indicator Detection is enabled in the environment.
FireEye Mandiant has been tracking DARKSIDE since August 2020 and proactively providing protection to customers as samples and techniques are discovered on the front lines during investigations by Mandiant. Customers should ensure they have configured and enabled FireEye products to protect against threats such as DARKSIDE using the information in this post. Additionally, Mandiant Managed Defense customers can reach out for assistance in configuring and operating FireEye products to provide maximum protection.
FireEye solutions and Mandiant services offer comprehensive coverage against DARKSIDE and other threats that matter most. Head over to our site to learn more about how FireEye Endpoint Security, Email Security, Network Security, and Helix, the FireEye security operations console, provide a layered approach to security that helps organizations see the bigger picture.
FireEye Endpoint Security 5.1 and FireEye Helix
With this release of FireEye Endpoint Security 5.1 and FireEye Helix, security operations are streamlined and contextualized. Helix provides a single unified view for threat detection, investigation and response to uncover threats across attack surfaces. Endpoint Security not only provides protection, detection and response, but also acts as a data collection and streaming source for Helix. Combining Helix and Endpoint Security enables detection, correlation of information, and prioritization of alerts.
Endpoint Security 5.1 builds upon the modular architecture introduced in Endpoint Security 5.0 by easing the management of modules and introducing new modules, providing greater detection to decrease the response time to a new threat. Additionally, Endpoint Security health status can now be displayed in Helix, reporting the health and running status of critical services.
With the prior release, deploying a new module meant Endpoint Security customers had to go to the FireEye Market to download and install the module before activation. Now, there is a new module tab in the Endpoint Security console where customers may choose whichever module they would like to activate and add it to their deployment. When modules become generally available, they will show up on the console (Figure 1) and an admin can deploy them seamlessly without additional steps.
Comprehensive Endpoint Security Module
Detection and investigation of threats can be centralized with a new Indicators of Compromise (IOC) Streaming module. With IOC Streaming, customers may now stream the metadata they would like back to Helix and store it for as long as needed to fully investigate a potential threat. This allows full threat hunting across multiple endpoints at the same time to ensure a threat is fully remediated.
This streamed data is available to use as part of an investigation that can be visually displayed in Storytime for Helix. Storytime provides a historical view of an alert and all the metadata events of the threat origin. With this view, security responders can trace the attack back to patient zero, find the cause and remediate. Once the threat is fully understood, the indicators can be used to find the footprints of the attack across the entire organization and clean up before the attacker can complete their mission. Streaming modules and Storytime for Helix are supported for Windows, macOS, and Linux endpoints.
A New Future for FireEye and Mandiant
By Joining Stg’s Portfolio Of Companies, The Fireeye Products Business Will Have An Opportunity To Accelerate Its Pivot Toward Becoming The Leading, Cloud-First Xdr Platform

With recent announcement of the sale of the FireEye Products business to Symphony Technology Group (STG), we have taken an important step forward to help us better serve our customers and accelerate strategies that are defining the future of cyber security.
The transaction will separate FireEye’s network, email, endpoint, and cloud security products, and related security management and orchestration platform from Mandiant Solutions’ controls-agnostic software and services. The result: both organizations will be able to accelerate growth investments, pursue new go-to-market pathways, and focus innovation on their respective solutions.
The transaction is expected to close by the end of the fourth quarter of 2021, and until then, the two organizations will continue to operate as a single entity, allowing for the FireEye Products business to make a smooth transition into the STG portfolio. Post-closing, the Company plans to rebrand as Mandiant. “By joining STG’s portfolio of companies, the FireEye Products business will have an opportunity to accelerate its pivot toward becoming the leading, cloud-first XDR platform extending across network, email, endpoint, and cloud security products, and the related security management and orchestration platform,” says Kevin Mandia, the CEO of FireEye. “STG’s focus on fueling innovative leaders makes them an ideal partner for FireEye Products – we clearly share a vision to build the world’s leading cyber security company. FireEye will be led by Bryan Palma, who joined us earlier this year as Executive Vice President of Products, along with his current leadership team.”
The two organizations will continue to share on critical information, with bi-directional sharing of threat intelligence and product telemetry to build and preserve competitive advantages that benefit the customers of both businesses. A joint reseller agreement will enable the FireEye and Mandiant sales teams to continue offering our integrated solutions. We have also established cooperative processes to make certain customer data is secure. In these and other ways, we will ensure that both parties have the resources necessary to deliver on – and exceed – customer expectations. “But the greater opportunities are ahead. I am proud of the progress our teams have made in protecting our customers and creating a safer world for the broader community with innovative technology, world-class intelligence and frontline expertise. I am convinced the best is yet to come as we see the newly independent FireEye and Mandiant build on these strengths,” concludes Mandia
July 27, 2021
Company
Fireeye
Management
Kevin Mandia, CEO
Description
FireEye Endpoint Security delivers advanced detection and prevention capabilities to help respond to threats that can bypass traditional endpoint defenses. With the addition of antivirus (AV) and malware detection capabilities for known threats, machine learning and behavioral analysis for unknown threats along with endpoint detection and response (EDR) capabilities, analysts can now rely on a single endpoint agent for expanded visibility to quickly determine the exact scope and level of attack activities related to both known and unknown threats