
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

Digital Edge Ventures
Turning Cybersecurity Operations into Continuous Compliance
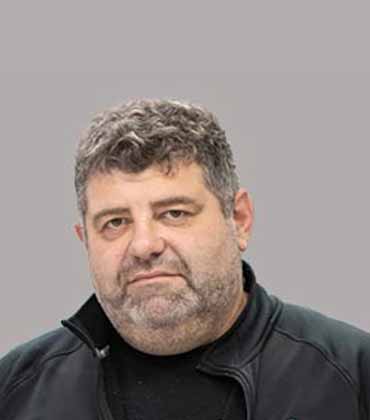 Michael Petrov, CEO
The harder part is keeping that proof organized as the business runs. Security work happens across alerts, tickets, reports, investigations and remediation efforts. Without a structured approach, businesses can find themselves reconstructing that activity when a customer or auditor asks for evidence. Digital Edge Ventures changes that by making compliance documentation part of normal security operations rather than something assembled at the end.
“Our main goal and proposition is to decrease the compliance burden on businesses that operate in regulated industries,” says Michael Petrov, CEO.
Each monitored alert, investigated incident, corrected vulnerability and documented response contributes to an ongoing record of how the business protects itself. When an audit or customer review arrives, that evidence already exists. The business can show what happened, how it responded and how its security controls operated over time.
“Too many organizations buy security tools first and hope they cover compliance later. We flip that completely. Regulatory requirements serve as our blueprint. We take those standards, make them work for our business and construct our security operations from the ground up,” explains Petrov.
“We’re very careful about not trusting AI,” says Petrov. “It’s not 100 percent AI processing. It’s a hybrid of algorithmical processing with AI triaging.”
The Engine Behind Continuous Compliance
Telemetry from client environments flows into a conventional SIEM, where established rules generate alerts. AI then evaluates each alert against client specific context, including the technology stack, available telemetry and operational history. When more detail is needed, it requests additional logs and reassesses before closing the alert or escalating it to an analyst. This hybrid model targets the triage bottleneck without replacing proven detection logic, with automated closures now averaging about 89 percent.

Too many organizations buy security tools first and hope they cover compliance later. We flip that completely. Regulatory requirements serve as our blueprint. We take those standards, make them work for our business and construct our security operations from the ground up.

“We’re very careful about not trusting AI,” says Petrov. “It’s not 100 percent AI processing. It’s a hybrid of algorithmical processing with AI triaging.”
Each month, Digital Edge conducts an internal audit of the previous period’s operations and produces three reports: an executive summary of attacks prevented and tickets resolved, a threat hunting review that manually checks logs the automated rules may have missed and a compliance report ready for an external auditor. Vulnerability management follows the same cadence, giving clients a unified rhythm for both detection and control validation.
One financial services firm needed to open a new office and was asked to prove GLBA compliance immediately. None of the required documentation existed. Digital Edge assembled the evidence package under tight deadlines and has kept the client audit ready ever since, now supporting SOC 2 reporting and emerging AI related compliance questions.
End To End Ownership
Digital Edge brings cybersecurity professionals, auditors and cybersecurity lawyers into one operating structure, so clients are not left coordinating separate providers for detection, remediation, incident response and compliance. Third-party tools may still be used when needed, but Digital Edge keeps management responsibility in one place.
That integrated model becomes especially valuable when technical work must satisfy regulatory requirements as well as security needs. After a HIPAA-regulated company experienced a security incident involving PHI, a generalist forensic firm resolved the technical issue but missed key HIPAA procedures, drawing scrutiny from the Office for Civil Rights. Digital Edge guided the company through HITRUST e1 certification and into i1 operation, with full i1 certification expected within a year.
End to end ownership runs through both use cases. Digital Edge assesses, remediates and operates without passing clients between separate teams, keeping accountability clear throughout the process. It provides full-service coverage for organizations with roughly 300 to 400 employees and supports, rather than replaces, existing security programs at larger financial institutions and banks. The pitch is not that Digital Edge eliminates risk. It is that risk becomes visible, documented and manageable long before a regulator or customer asks the question.
Security Operations Built for Continuous Compliance
Too frequently, when a client or regulator requests verification rather than just the protection regulated small and midsize firms find out the limitations of their security program. Despite having controls in place, a lender entering a new state, a fintech responding to a bank review, an insurer getting ready for a renewal or a health technology provider facing an audit may find it difficult to demonstrate that those controls are routinely implemented. The buying question is whether routine security work produces evidence that can withstand outside review without a separate scramble.
The first failure pattern is disjoint between compliance and cybersecurity. Security teams triage alerts and vulnerabilities, while compliance owners collect policies and evidence in a different workflow. This duplication adds cost for lean firms and a more serious vulnerability. Documented controls can diverge from the reality of what the security team does. In a stronger service model evidence capture is part of the work itself. Compliance records should be fed with alert disposition, vulnerability reviews, access changes and incident records as routine outputs and not reconstructed in the near of an audit.
Alert handling exposes a different procurement risk. If the customer environment is absent from triage, quick closure rates are meaningless. Depending on cloud topology, identity structure, application behavior and available telemetry, a single signal may entail varying degrees of risk. While automation aids analysts in gathering context and minimizing repetitive review, detection logic should continue to be based on predefined security criteria. The discipline of escalation is equally important. Instead of using automation percentage as a stand-in for security quality, a service should clarify what can be closed automatically and what needs to be sent to a human.
"Digital Edge Ventures feeds day-to-day security activity into audit-ready evidence, supported by monthly internal reviews and compliance reporting."
Continuous evidence changes the economics of compliance. Control performance collected during day-to-day security work can support customer reviews or regulatory requests without forcing staff to rebuild history from tickets and spreadsheets. Dashboard polish is secondary to the underlying mechanism. Executives should examine how evidence is generated, how often it is reviewed, whether identified gaps flow back into remediation and who owns follow-through. The enhanced model keeps the compliance record near to the security activity that produced it.
Service ownership becomes decisive when internal security staff is small. Coordinating consultants, tool suppliers, internal IT professionals and compliance advisers may be left to the client by a provider who only finds gaps. After corrections are made, findings should go straight into remediation and continue to be under accountable management. During an incident or audit, this continuity minimizes handoffs and maintains accountability. For regulated SMBs, the practical test is whether one provider can manage the work without forcing the client to build a large internal security function around it.
Digital Edge Ventures is the perfect partner for regulated SMBs to have security and compliance managed as one service. Its 24/7 SOC and MDR, continuous compliance monitoring, vulnerability management and incident response planning are aligned with those buying pressures. The service applies traditional SIEM rules at the detection layer. The AI then scores the alerts against the customer context, passing those the AI is unable to determine to the human analysts instead of automatically closing them out. Digital Edge Ventures transforms the security activity of the day-to-day into audit-ready evidence supported by monthly internal reviews and compliance reporting. It can also own the larger security and compliance program in smaller environments. That model offers executives who don’t have a large internal department a practical way to achieve sustained audit readiness and managed security coverage.
...Read more
Cybersecurity and Compliance Operations Solutions Info
Q1
What Are Cybersecurity and Compliance Operations Solutions?
Cybersecurity and Compliance Operations Solutions combine security monitoring, incident response, vulnerability management and compliance activities within a connected operating model. They help organizations detect threats while maintaining evidence that security controls are working over time. Cybersecurity and Compliance Operations Solutions can also reduce the need to reconstruct security activity when auditors or customers request documentation.
Q2
How Does Digital Edge Ventures Approach Cybersecurity and Compliance Operations Solutions?
Digital Edge Ventures builds Cybersecurity and Compliance Operations Solutions around regulatory requirements rather than treating compliance as a separate task. Its security operations use telemetry from client environments, conventional SIEM rules and AI-assisted alert evaluation. The system checks alerts against client-specific context and can request additional logs before closing an alert or escalating it. Automated closures average about 89 percent.
Q3
What Capabilities Are Included In Cybersecurity and Compliance Operations Solutions?
Cybersecurity and Compliance Operations Solutions can cover managed detection and response, security operations, cloud security, governance, vulnerability management and audit-ready evidence. At Digital Edge Ventures, monthly operations include an executive report, a manual threat-hunting review and a compliance report prepared for external auditors. This approach connects threat detection with ongoing control validation.
Q4
How Can Cybersecurity and Compliance Operations Solutions Support Continuous Compliance?
Cybersecurity and Compliance Operations Solutions can turn routine security work into a regular record of compliance evidence. Alerts, investigations, vulnerability fixes and documented responses add to this record. Digital Edge Ventures also conducts monthly internal audits and keeps documentation for customer reviews and regulatory assessments. For one financial services client, it prepared a GLBA evidence package under a tight deadline and later supported SOC 2 reporting.
Q5
Why Is Integrated Ownership Important In Cybersecurity and Compliance Operations Solutions?
Cybersecurity and Compliance Operations Solutions become more practical when security, remediation and compliance responsibilities remain connected. Instead of requiring separate providers for detection, incident response and compliance, an integrated model keeps management responsibility in one place. This can make accountability clearer when technical actions must also meet regulatory requirements.
Q6
How Does Digital Edge Ventures Apply Cybersecurity and Compliance Operations Solutions To Regulated Environments?
Digital Edge Ventures applies Cybersecurity and Compliance Operations Solutions to organizations that face regulatory and enterprise security requirements. It brings cybersecurity professionals, auditors and cybersecurity lawyers into one operating structure. In a HIPAA-related case involving protected health information, it guided the organization through HITRUST e1 certification and into i1 operation. It also provides full-service coverage for organizations with roughly 300 to 400 employees while supporting existing programs at larger financial institutions and banks.
Company
Digital Edge Ventures
Management
Michael Petrov, CEO
Description
Digital Edge Ventures is a cybersecurity and compliance operations firm that unifies 24×7 managed security with continuous regulatory compliance into one integrated, AI powered program. By combining MDR/SOC, cloud security, governance and audit ready evidence automation, the company helps organizations stay secure, compliant and commercially defensible year round. Digital Edge replaces fragmented tools and consultants with a single operational discipline that reduces risk, accelerates customer trust and ensures companies can confidently meet the demands of modern regulatory and enterprise grade environments.
