THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
The importance of Zero Trust Security
Jonathan Sanchez, CDPSE, Chief Information Security Officer, TRC Companies
1. What are some of the major challenges and trends that have been impacting the Zero Trust Security lately?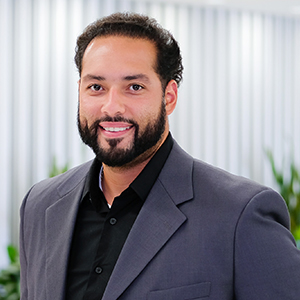 Jonathan Sanchez, CDPSE, Chief Information Security Officer, TRC Companies
Zero trust security is the concept of the “Always verify, Never trust” approach for network security. Essentially, ensuring that every user's device is always verified, regardless of whether they’ve previously been granted access. Zero trust security is the modern-day approach to protecting your network and organization's data. Outside of being one of the newest buzzwords in cyber security, successfully implementing Zero trust isn’t a turnkey solution (1) and requires a holistic approach to essentially start from the ground up. Deploying Zero trust can pose major challenges for firms as it’s not a set-it-and-forget solution. Locking down your network would be ideal but relies heavily on the ability to identify users, and devices, deploy monitoring tools, set up access controls, patch devices, and consistent management to reduce hidden gaps in protecting your network.
Implementing zero trust needs to be gradual to overcome deployment obstacles such as ongoing management (2). Zero trust is an approach, which calls for ongoing management to ensure ongoing protection. Zero trust adds enhanced security but can also impact staff performance (3). The potential for losing productivity comes with the need to continuously monitor and manage security settings. Adjusting firewall settings and access may enhance security but inadvertently lock out an entire department, which hinders the ability of workers to perform optimally.
Zero Trust security depends on secure hardware (4) to operate efficiently, part of implementing a zero-trust security framework involves securing your hardware. Patching and updating your existing boxes or deploying new devices altogether. Lastly, Zero Trust calls for flexible software (5). Organizations will have varying security solutions deployed and will often run into challenges with managing everything. Zero trust is an all-encompassing approach that provides added protection but also requires more overhead to manage.
2. What keeps you up at night when it comes to some of the major predicaments in the Zero Trust Security space?
Zero trust in today’s market is referred to by a fair amount of security professionals in many ways as a remedy for all the things that keep you up at night. Today’s risk landscape is consistently evolving and requires security teams to continue to elevate cyber postures to provide security for their corporate assets and network. Deploying a zero-trust network which provides the protection needed to help reduce the risk of a potential bad actor or compromise; helps reduce the looming thoughts that keep you from sleeping at night. Ideally, every CISO’s goal is to have the right solutions, processes, and resources in place, to allow time to sleep at night. Ongoing Zero trust development provides the ability to prepare for tomorrow as supposed to only focusing on today. Keeping business continuity at the forefront, while deploying security measures that don’t negatively impact productivity are reasons why I get out of bed each and every morning.
“Cybersecurity Continues To Evolve As Threat Actors Become More Resilient And Have Access To Malware Code, Which Can Be Leveraged To Enhance Or Deploy For Malicious Intent”
3. Can you tell us about the latest project that you have been working on and what are some of the technological and process elements that you leveraged to make the project successful?
Removal of legacy VPN solution and replacing it with an always-on solution, the system wasn’t designed to support an organization of 6k users, which needed to select the requested VPN of choice. Making the decision to upgrade the VPN to a solution to an always-on removed the need for users to make decisions regarding network access or data protection. In a perfect world, deploying a new VPN solution requires new segments, connectors built to manage traffic loads, and configuration changes to provide business access to applications. Change in companies typically comes with conflict and making a corporate VPN chance to securely manage data is no stranger to this process. Communication with deploying new solutions is key to successfully configuring the system and garnering business requirements to ensure system connectivity isn’t lost. Testing with user groups in pilot faces provides the ability to at a small scale simulate what would be expected for day-to-day operations. Unfortunately, testing doesn’t provide the production experience and new corporate solutions require phased deployments to manage project onboarding and bandwidth needs. Lastly, providing users with an open bridge on release day, ensure users have an SME (Subject Matter Expert) available to assist with potential issues not found during initial testing and deployment phases.
4. Which are some of the technological trends which excite you for the future of the Zero Trust Security space?
Zero trust continues to develop by adding new and upcoming features to help not only manage network security but also reduce the threat landscape by providing the ability to integrate with other solutions and vendors such as Microsoft. Early adopters of Zero Trust required major rebuilds to deploy a network built to protect against compromise. Zero Trust today now incorporates DLP (Data Loss Prevention) and Information protection capabilities which can be synced to Microsoft Azure Tenant. Patching is a required ongoing task expected to be done to ensure the environment is upkept but new developments allow devices to be segregated until required patches are deployed before passing a compliance check. Lastly, workloads can be connected to your environment and scanning engines will scan your pages to help manage posture and reduce cloud exposure.
5. Would you like to give a piece of advice to the community as to how should they approach this industry?
Cybersecurity continues to evolve as threat actors become more resilient and have access to malware code, which can be leveraged to enhance or deploy for malicious intent. Cybersecurity functions are created to help aid businesses in protecting trade secrets while securing networks and business uptime. Professionals should focus on developing a cybersecurity strategy, which aligns with business objectives to help provide secure technology as a service. For any individuals looking to enter the field, becoming a cyber asset is highly dependent upon the mindset and the ability to connect the dots and drive change which benefits the business while securing the corporate environment.