
THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

CrowdStrike [NASDAQ: CRWD]
Scaling AI-Native Security Operations
Enterprise security operations are increasingly defined by the need to manage continuous streams of activity across distributed environments. Endpoints, identities and cloud workloads generate constant signals, each requiring immediate interpretation to prevent escalation. Efficiency now depends on how effectively organizations can align visibility with response, ensuring that detection and action occur within the same operational cycle.
CrowdStrike [NASDAQ: CRWD] positions itself within this operational reality as a unified AI-native layer rather than a single-point solution. Its architecture reflects a shift from isolated tools to a unified system that continuously processes telemetry and converts it into real-time security decisions. The result is less about reacting to threats and more about orchestrating digital environments with consistency and speed.
Core Capability and Execution Model
The Falcon platform anchors CrowdStrike’s model, operating as a cloud-native system built on a single lightweight agent deployed across endpoints, workloads and identities. Rather than distributing multiple security tools across an organization, it consolidates data collection into one sensor that streams telemetry into a centralized cloud environment for analysis.
This architecture functions as a continuous data pipeline. Every endpoint action, identity event and workload interaction becomes part of a unified dataset. Within the platform, artificial intelligence models and behavioral analytics process this data in real time, identifying anomalies that indicate potential threats. Detection is not limited to known signatures; it relies on patterns, correlations and adversary behavior mapped against frameworks such as MITRE ATT&CK.
Execution follows a closed-loop system. Detection feeds directly into response. Through integrated orchestration capabilities, the platform can isolate compromised endpoints, enforce identity controls or trigger automated workflows without requiring manual intervention. Security teams operate within a single interface, where visibility, investigation and remediation are tightly linked.
The company extends this model through managed services such as Falcon Complete, where its own analysts operate the platform on behalf of customers. This introduces a hybrid execution layer combining automation with human expertise, ensuring continuous monitoring and response. The outcome is a system designed to function with minimal latency between signal and action, a requirement in environments where threats propagate rapidly.
Strategy and Differentiation
CrowdStrike’s strategic approach is rooted in consolidation and integration. Rather than expanding through disconnected products, it builds additional capabilities as modules within the same platform. Endpoint protection, identity security, cloud workload protection and data security all operate on shared infrastructure and data models.
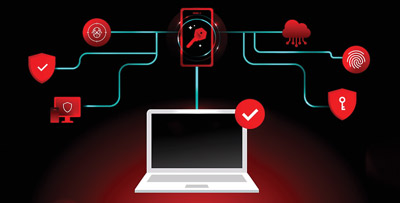 This unified design reduces operational friction. Organizations avoid the complexity of managing multiple agents, inconsistent data formats or fragmented workflows. Instead, the platform creates a single operational layer where different security domains intersect. Identity signals inform endpoint decisions. Cloud telemetry enriches threat context. Data movement becomes part of the detection logic.
Another distinguishing factor is the platform’s scalability. Because processing occurs in the cloud, the system can handle large volumes of telemetry without requiring significant on-premise infrastructure. This is particularly relevant for enterprises operating across hybrid and multi-cloud environments, where scale and flexibility are critical.
The company also emphasizes ecosystem integration. Through partnerships with major cloud providers and enterprise software platforms, Falcon connects with existing IT environments rather than replacing them. This allows organizations to extend security coverage without disrupting core operations.
Operational consistency further reinforces differentiation. The same detection logic, response mechanisms and data models apply across geographies and environments. Whether monitoring endpoints in a corporate network or workloads in a public cloud, the platform maintains a uniform approach. This consistency simplifies governance and enables organizations to enforce security policies at scale.
Impact and Application
The practical impact of CrowdStrike’s model becomes evident in how organizations respond to real-world threats. In a ransomware scenario, for example, the platform can detect abnormal behavior on an endpoint, correlate it with identity activity and isolate the affected system before the attack spreads. Automated workflows can simultaneously block malicious processes and alert security teams with contextual intelligence.
In cloud environments, the platform identifies misconfigurations or suspicious activity within workloads. By linking these signals to known adversary tactics, it prioritizes remediation efforts based on risk rather than volume. This reduces the time required to identify and address vulnerabilities.
Identity-based attacks present another application. As attackers increasingly exploit credentials rather than software vulnerabilities, the ability to monitor user behavior becomes critical. CrowdStrike’s approach integrates identity signals into its detection framework, enabling real-time enforcement of access controls when anomalies are detected.
Data protection represents a further extension of this model. By treating data movement as a security signal, the platform can detect and prevent unauthorized transfers across endpoints, browsers and cloud applications. This aligns with the growing importance of safeguarding sensitive information in distributed environments.
Across these use cases, the measurable outcome is a reduction in response time and operational complexity. Security teams spend less time correlating data from multiple systems and more time acting on prioritized insights. The platform’s automation capabilities also reduce manual workload, allowing organizations to maintain effective security operations with leaner teams.
The broader implication is a shift in how cybersecurity is managed. Instead of reacting to isolated incidents organizations operate within a continuous monitoring and response framework. This approach supports resilience by ensuring that detection and remediation occur as part of an integrated process rather than a series of disconnected actions.
In an industry defined by rapid change and increasing complexity, consistency in execution becomes a defining advantage. CrowdStrike’s ability to unify data, automate response and scale across environments reflects a disciplined approach to cybersecurity operations. That consistency, combined with measurable outcomes in detection and response, positions the company as a clear example of AI-native cybersecurity in practice, where intelligence and execution operate as a single system.
Company
CrowdStrike [NASDAQ: CRWD]
Management
George Kurtz, CEO and Founder
Description
The CrowdStrike executive team is comprised of savvy business leaders and security industry experts, bringing years of experience together to create security solutions that just work. They cultivate our strong culture and work tirelessly to protect enterprises and governments from advanced threats and targeted attacks with cutting-edge technologies and professional services.

