THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

ControlPlane
Gain Control Over Cloud Security
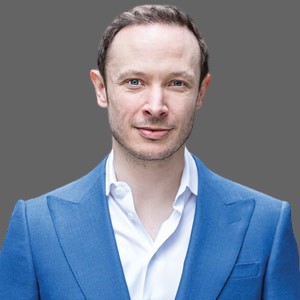 Andrew Martin, CEO
This change impacted many systems’ security, including firewalls, VPNs, and applications, and gave ControlPlane the opportunity to help customers implement zero trust architectures from a workload identity perspective, using SPIFFE and SPIRE technologies and service mesh concepts integrated by Istio and Cilium. ControlPlane is a cloud native security consultancy that had its genesis with a team building critical national infrastructure for the UK government in 2015. Today the team provides industry-leading expertise in building, deploying, and maintaining high compliance Kubernetes and cloud native systems. As cloud native systems require SDNs, so removing the link between IP address and a workload’s “identity”, a new trusted identity is required to secure network traffic.
By issuing unique cryptographic identities per workload, the firm’s solutions secure IT systems irrespective of the IP address allocation, and enable zero-trust workloads throughout. This gives applications the opportunity to mutually validate every inbound network connection using protocols such as TLS, with certificates that can be frequently rotated. As a result, in the event of a compromise of a workload, there is only a short period of time when the stolen credentials can be reused, and passwords are no longer required. “The greatest challenge for many customers was the move to remote work during the pandemic, as it relies heavily on VPNs to authenticate users into corporate systems from potentially untrusted remote networks,” says Andrew Martin, the CEO.
The workloads and websites are hidden behind a proxy set up by the firm, granting access based on a user’s identity as given by their email, which by default involves two-factor authentication.
In the case of private Kubernetes clusters, a Bastion is set up behind an Identity Aware Proxy, such that a user can transit through to a private network hidden behind the Proxy.
This solution increased the resilience to compromises and enabled the customer to harden single dangerous points of exploitation. It increased their confidence in feature releases by virtue of verifying and validating all the supply chain components that were deployed. Interestingly, to provide a real-world threat-based guide on attacking and defending Kubernetes clusters, Andrew Martin, with his friend Michael Hausenblas (Solution Engineering Lead, AWS), recently published a book called ‘Hacking Kubernetes.’
In the event of compromise, the blast radius of the attack is limited to that particular network or account, instead of exposing the network of an entire organization. A customer approached ControlPlane wanting to remove password-based authentication and introduce workload identity for a global fleet of container services. The customer had identified a risk affecting various parts of their network architecture that could potentially lead to the compromise of internal systems. To eliminate present or future threats, ControlPlane ensured that the application and platform CI/ CD and software supply chain met the required security guidelines, including production deployment flow verification and the validation of cryptographically signed artefacts at deployment time. “A robust workload identity framework such as SPIFFE’s SPIRE was set up based on Open Policy Agent, that together provided the client with a highly flexible authentication and authorization framework,” says Martin.

A robust workload identity framework such as SPIFFE's SPIRE was set up based on Open Policy Agent that provided the client with a highly flexible authentication and authorization framework

This solution increased the resilience to compromises and enabled the customer to harden single dangerous points of exploitation. It increased their confidence in feature releases by virtue of verifying and validating all the supply chain components that were deployed. Interestingly, to provide a real-world threat-based guide on attacking and defending Kubernetes clusters, Andrew Martin, with his friend Michael Hausenblas (Solution Engineering Lead, AWS), recently published a book called ‘Hacking Kubernetes.’
The book was penned with the goal of assisting industry engineers in identifying, classifying and removing threats from cloud native systems. ControlPlane plans to launch various products and open-source projects addressing newer requirements within the enterprise realm. “We believe that zero trust workload identity principles will mature so they are enshrined in network security across clouds, assisting workload immunity to credential compromise and hardening to attack,” says Martin. ES

Company
ControlPlane
Management
Andrew Martin, CEO
Description
ControlPlane assists customers implementing secure, zero-trust platforms and infrastructure using SPIFFE and SPIRE technologies.They provide industry-leading expertise in building, deploying, and maintaining high compliance Kubernetes andcloud native systems, security audits and assessments, and specialised security training.ControlPlane provides industry-leading expertise in building, deploying, and maintaining high compliance Kubernetes and cloud native systems. As cloud native systems require SDNs, so removing the link between IP address and a workload’s “identity”, a new trusted identity is required to secure network traffic