THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Strengthening Enterprise Security via a Multi-Faceted Approach
David Jenkins, Chief Information Security Officer,The Lottery Corporation
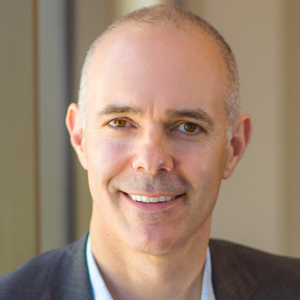 David Jenkins, Chief Information Security Officer,The Lottery Corporation
David Jenkins delved into the world of enterprise security over two decades ago when he was still working as a computer programmer. Jenkins has had a strong and steady career path, working his way right from being a security analyst to becoming the CISO of Tabcorp and then The Lottery Corporation.
Over his career, Jenkins has served in many technical security and security management roles in leading companies and institutions. He has primarily held senior information security roles in the banking and financial services sector, having worked with ANZ, GE Capital, CBA, the London Stock Exchange, and health insurer Bupa.
What according to you are some of the challenges plaguing enterprises today?
In all my years in the security landscape, what seems to be the leading issue for organizations is the need to keep pace with new attacks and threats. Even though defenses are established,and initially they show tremendous results, over time however, with the growing sophistication of attacks, these security models fail to deliver the intended results. Today, it is a constant arms race between the perpetrators and organizations.
Companies also face risks around disruptions in technology services. For instance, if they have a Denial-of-Service (DoS) attack, it would disrupt the essential business services and hamper their revenue generation and bottom line. There is also the prevalence of other attacks where a malicious actor tries to retrieve customers’ confidential information. In such cases, companies need to be proactive to detect such activities and be able to effectively stop them in time.
How can organizations effectively combat these issues?
With the growing sophistication, number, and types of attacks, it is only logical to take a multifaceted approach to resolve any security breach. One of the aspects is around providing limited access to the company’s network and ecosystem. Traditionally, giving remote access to employees meant full access to the company’s network. This essentially expanded the attack surface and made companies more vulnerable. Therefore, it is necessary to provide just enough access for the staff to carry out their operations. As such, if any of their systems are compromised, the attack will be restricted to a limited area of access rather than infiltrating the entire network. This also applies to third-party stakeholders, who should be given limited access to perform their operations.
In conjunction with that, it is paramount for organizations to have strong authentication measures, including second-factor authentication, to stop many of these attacks in the first instance. The companies also need to take a proactive approach to quickly detecting and blocking these attacks in time, right at the network perimeter. They must develop capabilities to identify legitimate traffic, get automatic alerts, and block illegitimate access to their network. This is more significant in today’s business landscape because of the increasing traffic going through network gateways daily, which makes it almost impossible to manually review all the alerts. In such cases, organizations need to adopt new technologies to detect these anomalies and automatically block them. They must enforce the right gateway controls and defenses, especially given the sheer number of attacks.
"Organizations should have a framework that goes beyond technology to include everything from legal, regulatory, communication, and other business aspects that need to work in concert to respond successfully to incidents"
Another important aspect is to be completely prepared with a robust incidence response process that is well-defined and has clear responsibilities and communication among all team members. In case of a major incident, organizations should have a framework that goes beyond technology to include everything from legal, regulatory, communication, and other business aspects that need to work in concert to respond successfully to incidents.
How has your company been at the forefront of strengthening its security posture?
One of the biggest risks for organizations today is ransomware attacks; no company is immune to this threat. To combat this, we started implementing a number of controls and uplifting existing ones in our security program to properly defend our infrastructure in case of a ransomware attack. We have rolled out several capabilities, including endpoint detection response and new technologies allowing experts to come in and support the business environment, manage, and contain any breaches. In conjunction, we have implemented security event and information management capabilities to see all the logs from different infrastructure components from various application levels and pull them together in a centralized system to alert on key events. This has allowed us to have visibility of what is happening in the business environment and respond appropriately to any incidents.
What are some of the future disruptions that will take place in the security landscape?
One of the areas that isrequiring focus is cyber insurance. It is becoming more difficult for companies to get cyber insurance or renew it because of the growing number of cyber attacks. In such cases, these organizations maynot have the required funds to set aside a certain amount to recover from a large incident.
A constant challenge in my experience, as we introduce new technologies, the attackers continually work out ways of circumventing them. Now more than ever, it is essential for companies to have defense in depth controls consisting of people, process and technologies to protect their organizations sufficiently.
Is there a piece of advice you would like to share with industry leaders?
In my opinion, cybersecurity and information security are very technical fields.We, the leaders, must have sound comprehensive knowledge across the entire field. Moreover, what is most critical is the people aspect. It is vital to have strong stakeholder management, to influence and win support for uplifting the cyber position, build strong relationships with their immediate teams, and continue supporting, coaching, and giving them clear directions around what’s required. It is also paramount to get the buy-in from the executives and the board and win their confidence so they can trust their security executives, ultimately investing and funding their security programs. This is crucial in protecting one’s organization.