THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Giving Cybersecurity a Business Lens
Grant McKechnie, Chief Information Security Officer at Endeavour Group
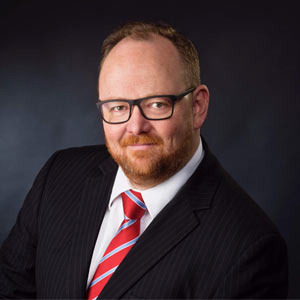 Grant McKechnie, Chief Information Security Officer at Endeavour Group
Until recently, financial companies and government agencies were the prime targets of cyber attacks. Now, almost every industry increasingly relies on the internet and cloud-based technologies, and it is safe to say that today's threat actors spare no one. Bad actors continuously devise new ways to circumvent security controls and gain access to an organisation's network and data, whether it be to damage, disrupt or steal data or other assets.
One way to mitigate this effect is by bringing a business lens into enterprise security. Building partnerships with the business and understanding what it is they are trying to achieve.
As the CISO of Australia’s leading retail drinks and hospitality business, Endeavor Group, this approach has helped us better structure our cybersecurity capabilities following the demerger from Woolworths Group in 2021. The past year was particularly challenging for us since we had to ensure our new company had the proper cyber defence mechanisms to weather any cyber threat or attack. This was a Greenfield Implementation at a scale that required a lot of thought and effort. We had to build a team as I was Cyber employee number one. We now have a great team working on this and have developed appropriate levels of defence and the right solution for our new standalone business.
Another advantage that helped me in leading the team in this initiative was my experience in handling many Greenfield Implementation projects. Before moving into cybersecurity, I worked as a technical architect in London. Then I donned the role of project manager for vulnerability management for BP, also in London. It was a Greenfield project with many novel challenges, and it was this project that piqued my desire to move into cybersecurity. After moving back to Australia, I have worked in cybersecurity with several private organisations and government agencies for over twenty years.
A significant milestone in my career was the role of GM - Operational Security for Australia's largest infrastructure programme, the National Broadband Network (NBN). It is the single most challenging role to date in my career. The areas of responsibility included providing NBN advice to the satellite solutions through to Data centres and the Active NBN network. A highlight of my tenure at NBN was delivering a leading-edge Security Operations Centre with advanced detection and incident management capabilities. Other experiences that have been pivotal in highlighting the critical importance of cybersecurity to an enterprise’s operations have been previous roles with several financial institutions, including Chase Manhattan and National Australia Bank (NAB).
The responsibility of CISO has always been a career goal for me. And now in this role with Endeavor Group, I'm entrusted with building the greenfield function for the company's cyber security environment. With the function now established, we operate as a high-performing team, ensuring the security of many brands that operate as part of the Group.
“I believe bringing a business lens to enterprise security helps companies reduce their cybersecurity risk and build solutions that best suit their individual and unique needs”
Through my decades of experience working in cybersecurity, I’ve been fortunate to see the significant development the industry has undergone. But there have been challenges also, and one of the more significant challenges the industry faces today is in recruiting the talent needed to support the industry’s growth. And while it’s important to recruit those experienced candidates to fill key roles, it’s just as important to think about building that pool of cyber talent from within an organisation. At Endeavor Group, we employ more than 28,000 people, and we have a robust internal program to identify and support those team members interested in a career in cyber, where we can help to train and develop them to become security specialists. As a result, we’re already achieving fantastic results developing emerging talent to become key members of our cybersecurity team.
Another challenge that’s quite prevalent at present is the increase in bad actors from outside the Asia Pacific region engaging in reconnaissance activities, as they consider countries such as Australia and New Zealand soft targets. Again, an effective way to tackle this is to address it from a business perspective rather than a systems perspective. By considering cybersecurity an essential value-added service, rather than an exercise in insurance, businesses will be able to operate at pace in a safe and secure manner.
The final piece of advice for my fellow CISO’s is to take the time to really understand your organisation’s line of business – the products and services your organisation provides, your customers and other key stakeholders, and really understand what the broader business risks are, beyond the cyber risks. By taking this holistic approach, as a CISO you’ll be much better positioned to develop an effective cybersecurity strategy that is fit-for-purpose for your organisation and which takes into account all the necessary considerations. This is where having a business lens is critical. Moving forward, I believe cybersecurity skills will be more democratized across different business disciplines, whether finance, operations, or management, for example. As such, as a CISO, we need a business lens to help us better align with the market changes.