THANK YOU FOR SUBSCRIBING
× 
Enterprise Security Mag Weekly Brief
Be first to read the latest tech news, Industry Leader's Insights, and CIO interviews of medium and large enterprises exclusively from Enterprise Security Mag
Enterprise Security Magazine

Access Quality
Building Stronger Security Foundations through DDI
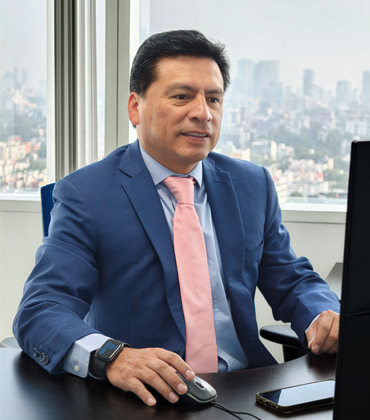 Omar Carrillo Perea, Commercial Director
Access Quality addresses this gap by integrating DNS, DHCP and IPAM into a unified DDI environment with native security capabilities. Rather than treating DNS security as an isolated layer, it helps enterprises validate queries, identify malicious activity and strengthen visibility, control and resilience.
“Our solutions transform DNS from a blind spot into a proactive layer of defense against threats,” says Omar Carrillo Perea, Commercial Director.
Beyond technical implementation, Access Quality brings experience in Mexico and Latin America to deployments where network complexity, local requirements and operational realities can vary significantly. Through specialized technical support, training and solutions adapted to local regulatory requirements, it helps enterprises implement and manage security capabilities without relying solely on external expertise.
Strengthening Networks Through Tailored Security Solutions
Each DDI implementation is tailored to the customer’s existing network environment. For organizations operating legacy DNS environments, Access Quality can modernize network management through overlay deployments rather than requiring replacement.
It implements solutions such as BlueCat Integrity DDI and Micetro DDI to provide enhanced visibility, automation and centralized control across on-premises, cloud and hybrid environments. Integration with RESTful APIs and third-party systems further reduces manual work and helps security teams apply consistent policies across distributed infrastructure.
In its implementations, Access Quality integrates BlueCat DNS Edge with Cisco Umbrella to strengthen security across internal and external DNS traffic. BlueCat DNS Edge acts as the initial recursive server for internal DNS records, helping security teams identify the origin of outgoing queries, locate infected devices and visualize internal east-west queries that may not pass through Cisco Umbrella's cloud security platform.
By extending Cisco filtering policies to network endpoints and sending DNS query logs to the customer's SIEM, the implementation supports the detection, investigation and remediation of threats like data exfiltration and unauthorized access. This joint solution is implemented in less than one week, simplifying threat detection and content filtering, while shortening SOC investigations.

Our solutions transform DNS from a blind spot into a proactive layer of defense against threats.

In one instance, a large-scale logistics organization faced critical security challenges. Limited visibility into internal DNS traffic and DNS-based data exfiltration made data correlation more complex. This extended digital forensic investigations to an average of eight days.
Access Quality implemented BlueCat DNS Edge as a security layer at the first hop of each query, allowing it to monitor approximately 3.2 million internal queries per day and automate policies to block malicious or anomalous behavior. The solution also began blocking DNS tunnels, Domain Generation Algorithms and other data exfiltration signatures, averaging 720 blocks per hour.
The average forensic investigation time fell from eight days to six hours, enabled by a searchable record of DNS queries and responses that simplified investigation and correlation. The client’s DNS data was made available in their Splunk platform for analysis, with direct connection to real-time mitigation from the solution interface. The organization’s DNS was transformed from an underutilized protocol into a real-time threat intelligence source.
Optimizing Network Resilience
Access Quality also focuses on network resilience through integrated DDoS mitigation and DNS infrastructure redundancy. Additionally, its ability to connect solutions with firewalls and security tools, including Cisco ISE, further strengthens this layered defense.
Clients often highlight its rapid deployment capabilities and integrated protection, which brings security closer to the DDI layer rather than requiring a separate, isolated DNS security environment.
By turning DNS visibility into actionable threat intelligence and integrating security with the network layer, Access Quality helps enterprises detect, investigate and respond to threats more effectively.
Securing DNS Traffic across Hybrid Networks
DNS has become harder to police as application traffic moves between corporate networks and cloud environments. Security teams may inspect internet-bound requests while retaining limited visibility into internal DNS activity, leaving lateral traffic harder to trace. That gap matters when malicious domains, DNS tunneling or compromised endpoints use ordinary name resolution as a path around controls. Executives evaluating DNS traffic security should look beyond external filtering and ask how much of the actual query path the security layer can see.
Visibility begins with knowing which device generated a query and where that request traveled. Internet-only inspection can miss traffic that remains inside the enterprise, particularly in distributed networks where applications depend on internal DNS records. Useful protection needs coverage at the point where queries originate, supported by searchable logging that gives security teams enough context to investigate suspicious behavior. DNS data should also feed existing security tools rather than create another isolated console. Integration with SIEM platforms and established security controls can shorten the path from detection to investigation.
Hybrid infrastructure creates a separate purchasing problem. Enterprises rarely operate on a clean network built around one architecture. Legacy DNS services may remain in place while workloads spread across data centers and public clouds. Replacing that infrastructure can introduce migration risk and delay security improvements. A practical DNS security platform should be able to sit over existing environments, centralize policy and extend control without forcing an immediate rebuild. API access also matters because repetitive DNS administration becomes costly when changes across large networks still depend on manual intervention.
“Access Quality layers centralized DNS control over existing infrastructure without forcing buyers into a wholesale replacement.”
Availability deserves equal scrutiny, as DNS protection cannot become another point of failure. Traffic surges and denial-of-service attacks can disrupt access even when the application infrastructure remains healthy. Buyers should examine how DNS security handles sudden demand, distributed environments and malicious traffic while preserving response availability. Policy enforcement also needs to remain consistent as applications move between locations. A security model that works only in one cloud or inside the corporate network leaves the enterprise managing different rules across the same service path.
Regional deployment adds another layer of complexity. Large organizations may need local technical support, training for internal teams and deployment choices that reflect existing network designs. The quality of implementation matters here as much as the underlying technology. Centralized control has limited value if internal teams cannot maintain policies or investigate events once the initial project ends.
Access Quality fits this buying logic through BlueCat-based DDI and DNS security deployments that combine DNS control with DHCP, IP address management and native protection. BlueCat DNS Edge can inspect internal and external DNS activity while forwarding logs into SIEM environments and working alongside Cisco Umbrella.
It layers centralized DNS control over existing infrastructure without forcing buyers into a wholesale replacement. Its use of BlueCat Micetro DDI and Integrity DDI also supports hybrid and multi-cloud management, while RESTful API integration helps reduce manual administration. For enterprises that need broader DNS visibility without rebuilding the network underneath it, that combination merits close consideration.
...Read more
DNS Traffic Security Solutions in Latin America Info
Q1
What Are DNS Traffic Security Solutions in Latin America?
DNS Traffic Security Solutions in Latin America secure the domain-name resolution layer that connects users, devices, applications and services. They let security teams monitor DNS requests, flag suspicious domains, detect tunneling and data-exfiltration attempts and apply policies closer to where queries begin. DNS Traffic Security Solutions in Latin America are especially useful in hybrid environments, where requests can move across internal networks, cloud platforms and the internet.
Q2
How Does Access Quality Approach DNS Traffic Security?
Access Quality brings DNS, DHCP and IP address management together in a unified DDI environment with security controls at the network layer. Its implementations use BlueCat DNS Edge, BlueCat Integrity DDI and Micetro DDI. It also integrates DNS Edge with Cisco Umbrella and can send DNS query logs to SIEM platforms. For organizations evaluating DNS Traffic Security Solutions in Latin America, this approach places DDI security within the wider network rather than treating it as a separate control.
Q3
What Problems Can DNS Traffic Security Solutions in Latin America Help Solve?
A common gap appears when security teams can see internet-bound requests but have limited visibility into internal DNS activity. DNS Traffic Security Solutions in Latin America can help trace queries to the devices that generated them, flag malicious or unusual behavior, block DNS tunnels and Domain Generation Algorithms and support investigations through searchable query records. They can also reduce manual work when DNS policies and changes span distributed infrastructure.
Q4
What Should Organizations Evaluate When Choosing DNS Security Technology?
Start with query visibility, logging depth, SIEM integration, policy enforcement, API support, resilience and compatibility with existing infrastructure. DNS Traffic Security Solutions in Latin America should work across on-premises, cloud and hybrid environments without requiring an immediate network replacement. Organizations should also consider regional implementation support, technical training and how easily teams can maintain policies after deployment. DNS security is most useful when it fits the existing network and security workflow.
Q5
How Did Access Quality Demonstrate the Value of This Model?
Access Quality applied BlueCat DNS Edge for a large logistics organization that had limited visibility into internal DNS traffic and difficulty investigating DNS-based data exfiltration. The deployment monitored about 3.2 million internal queries per day and averaged 720 blocks per hour against DNS tunnels, Domain Generation Algorithms and other exfiltration signatures. Average forensic investigation time fell from eight days to six hours. The case shows how DNS Traffic Security Solutions in Latin America can turn DNS records into a practical source for threat detection and investigation.
Q6
How Can DNS Traffic Security Solutions in Latin America Support Network Resilience?
DNS protection needs to remain available during traffic surges, distributed operations and denial-of-service events. DNS Traffic Security Solutions in Latin America can support this by combining DNS security with infrastructure redundancy, DDoS mitigation, centralized policy control and integration with existing firewalls and security tools. Access Quality also uses overlay deployments for some legacy environments, allowing organizations to modernize DNS management without immediately replacing the underlying infrastructure. This approach can extend security controls while limiting migration disruption.
Company
Access Quality
Management
Omar Carrillo Perea, Commercial Director
Description
Access Quality delivers enterprise DDI and network security solutions that integrate DNS, DHCP and IP address management with native security capabilities. Through regional expertise, technical support and tailored implementations, the company helps organizations strengthen visibility, resilience and operational efficiency across complex network environments.